Security Research Platform · CyberLynk LLP · Made in India
Partha
Partha is a single native desktop application that bundles a full web-application security-testing suite plus binary reverse-engineering, comparable in scope to a professional web-security workbench. It runs completely offline - nothing leaves your machine except the traffic you deliberately send to your targets (and, optionally, a single upload to the decompiler service described in §6.21).
Download
Partha runs locked until it is activated with a license issued by CyberLynk. Check the SHA-256 of the file you downloaded against the value shown here.
Windows
Windows 10 / 11 (64-bit)
SHA-256
e3b1291509191f15f4806fdab2148299669b89a2e2782f0b8e209b9819030474SHA-256
4e1e39144214911a128e476621353287d81a12d8534ed672f98a0ab8ad68a2eaVerify: certutil -hashfile <file> SHA256
Linux
64-bit Linux (Ubuntu 22.04+, Debian, Fedora…)
SHA-256
0f5ae45abdf799e6c8e513aabc6b56a04098d835f8a1e57359ac8185b6e9a786SHA-256
7b14d53ac74e50b0fa585b8737d68739f28cbf396e78e186a4fb709f84bdb45bVerify: sha256sum <file>
The Partha workbench
What Partha can do
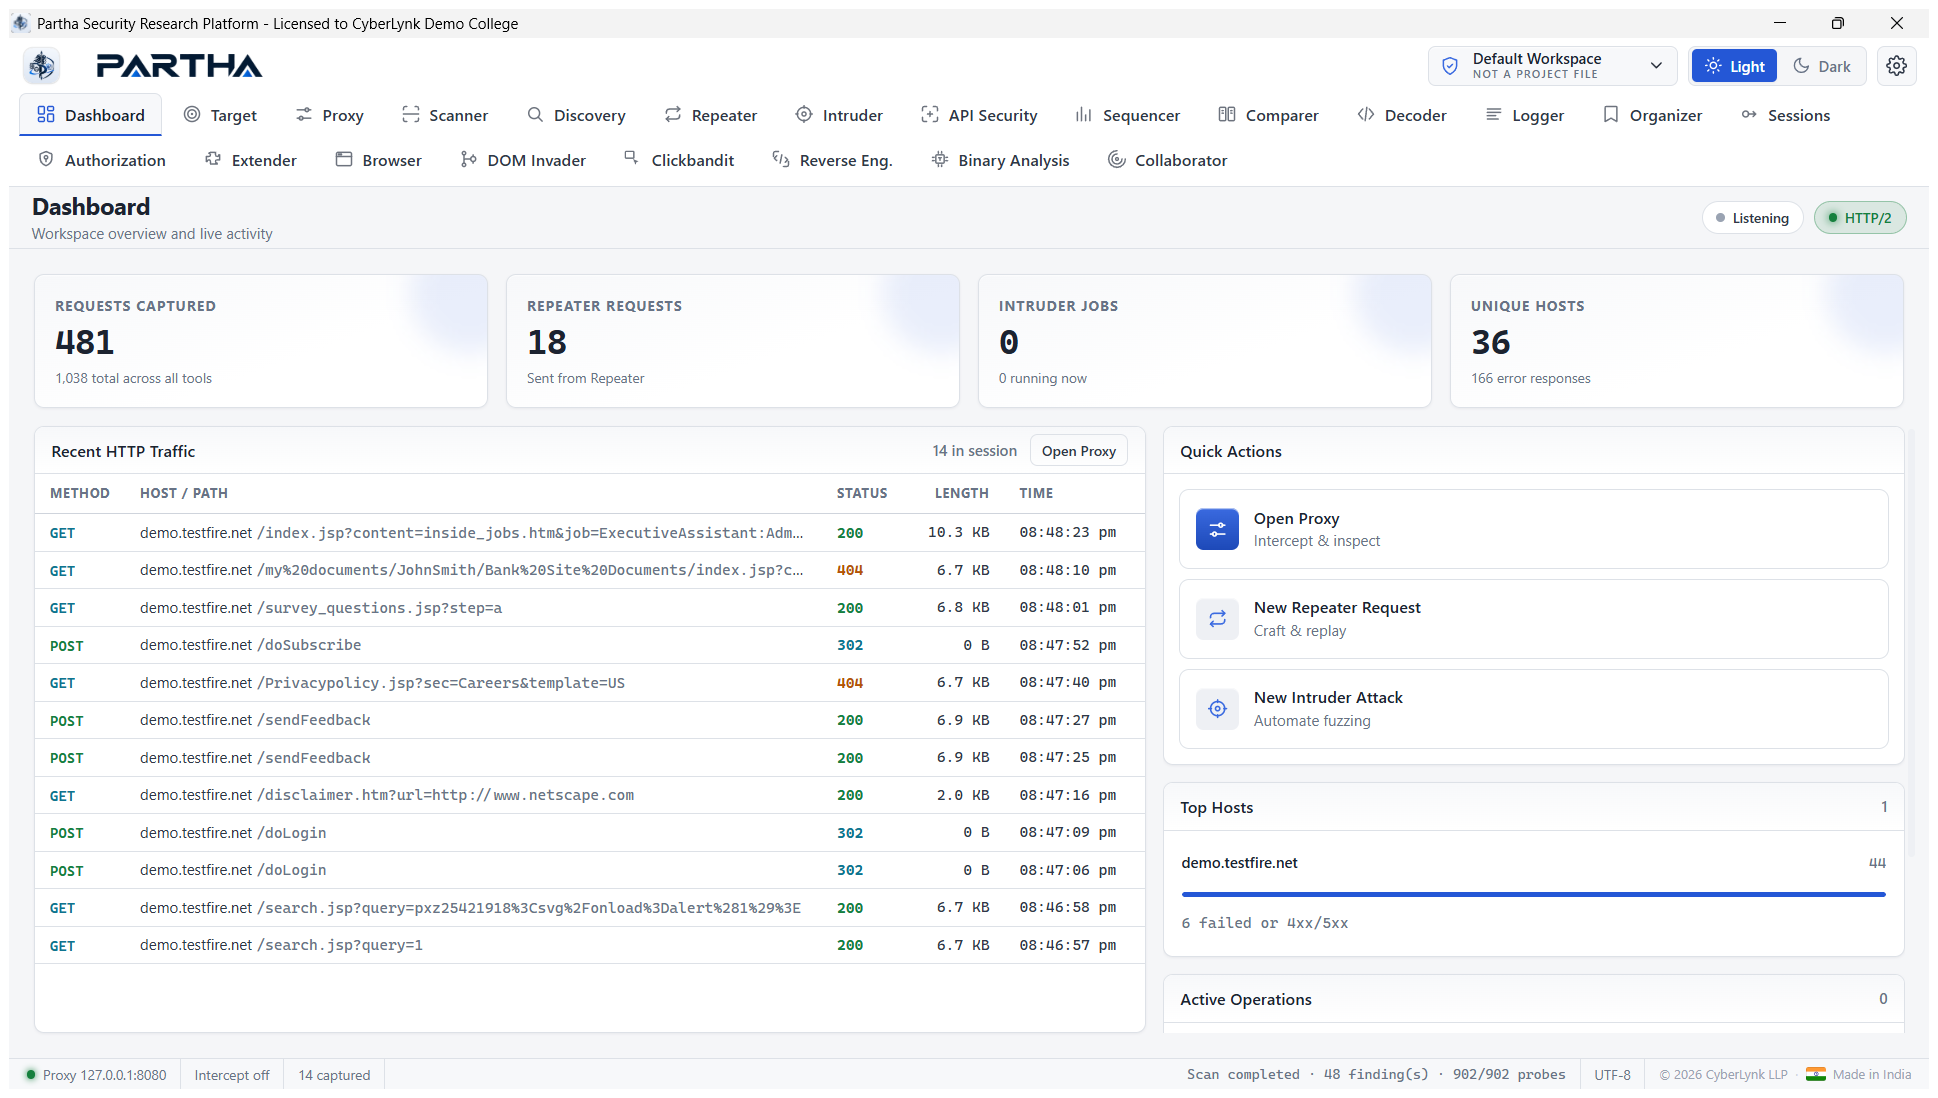
Dashboard
Live operational overview; every figure is derived from real state.Dashboard with live testfire dataStat tiles — Requests captured (and total across all tools), Repeater requests, Intruder…
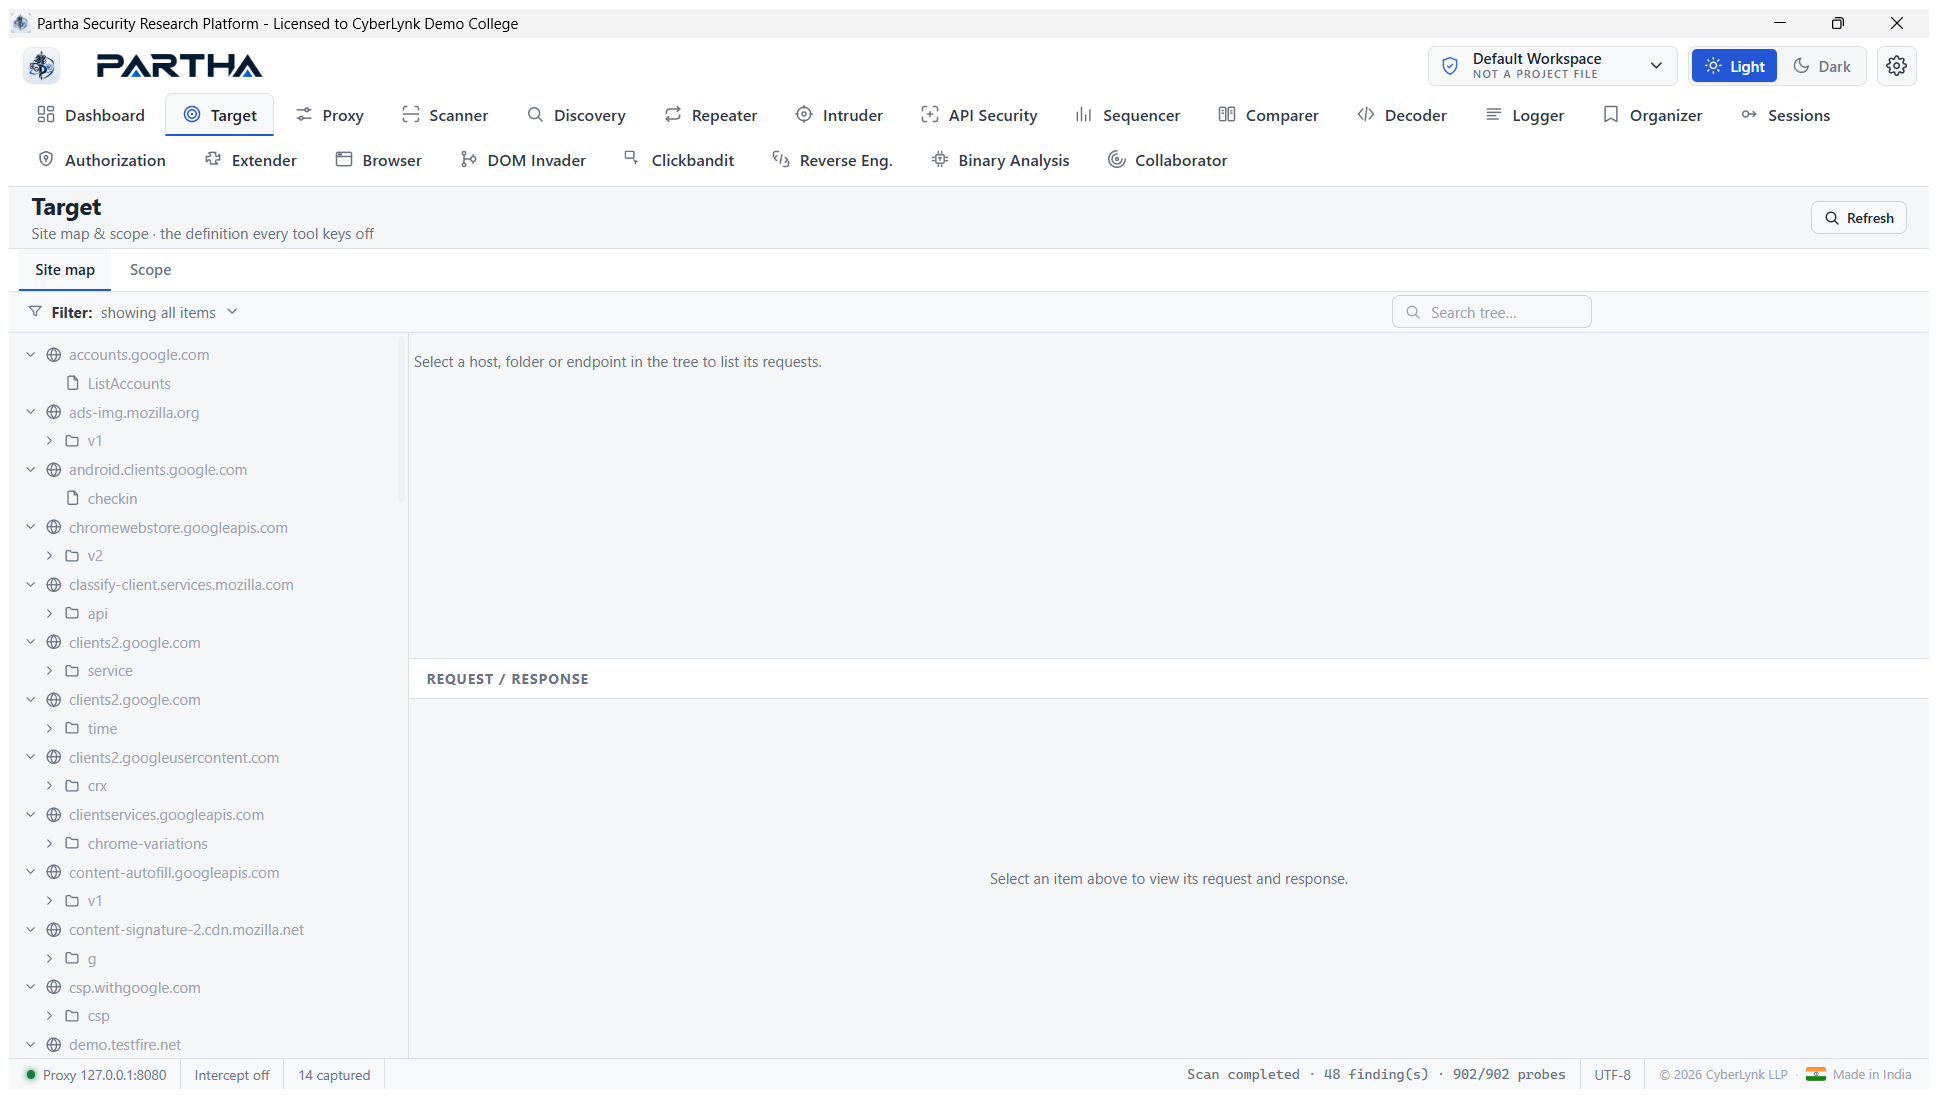
Target — site map & scope
Site map — a per-host tree built automatically from all captured traffic. Select a node to list its requests and inspect request/response.Target site mapScope — the definition every other…
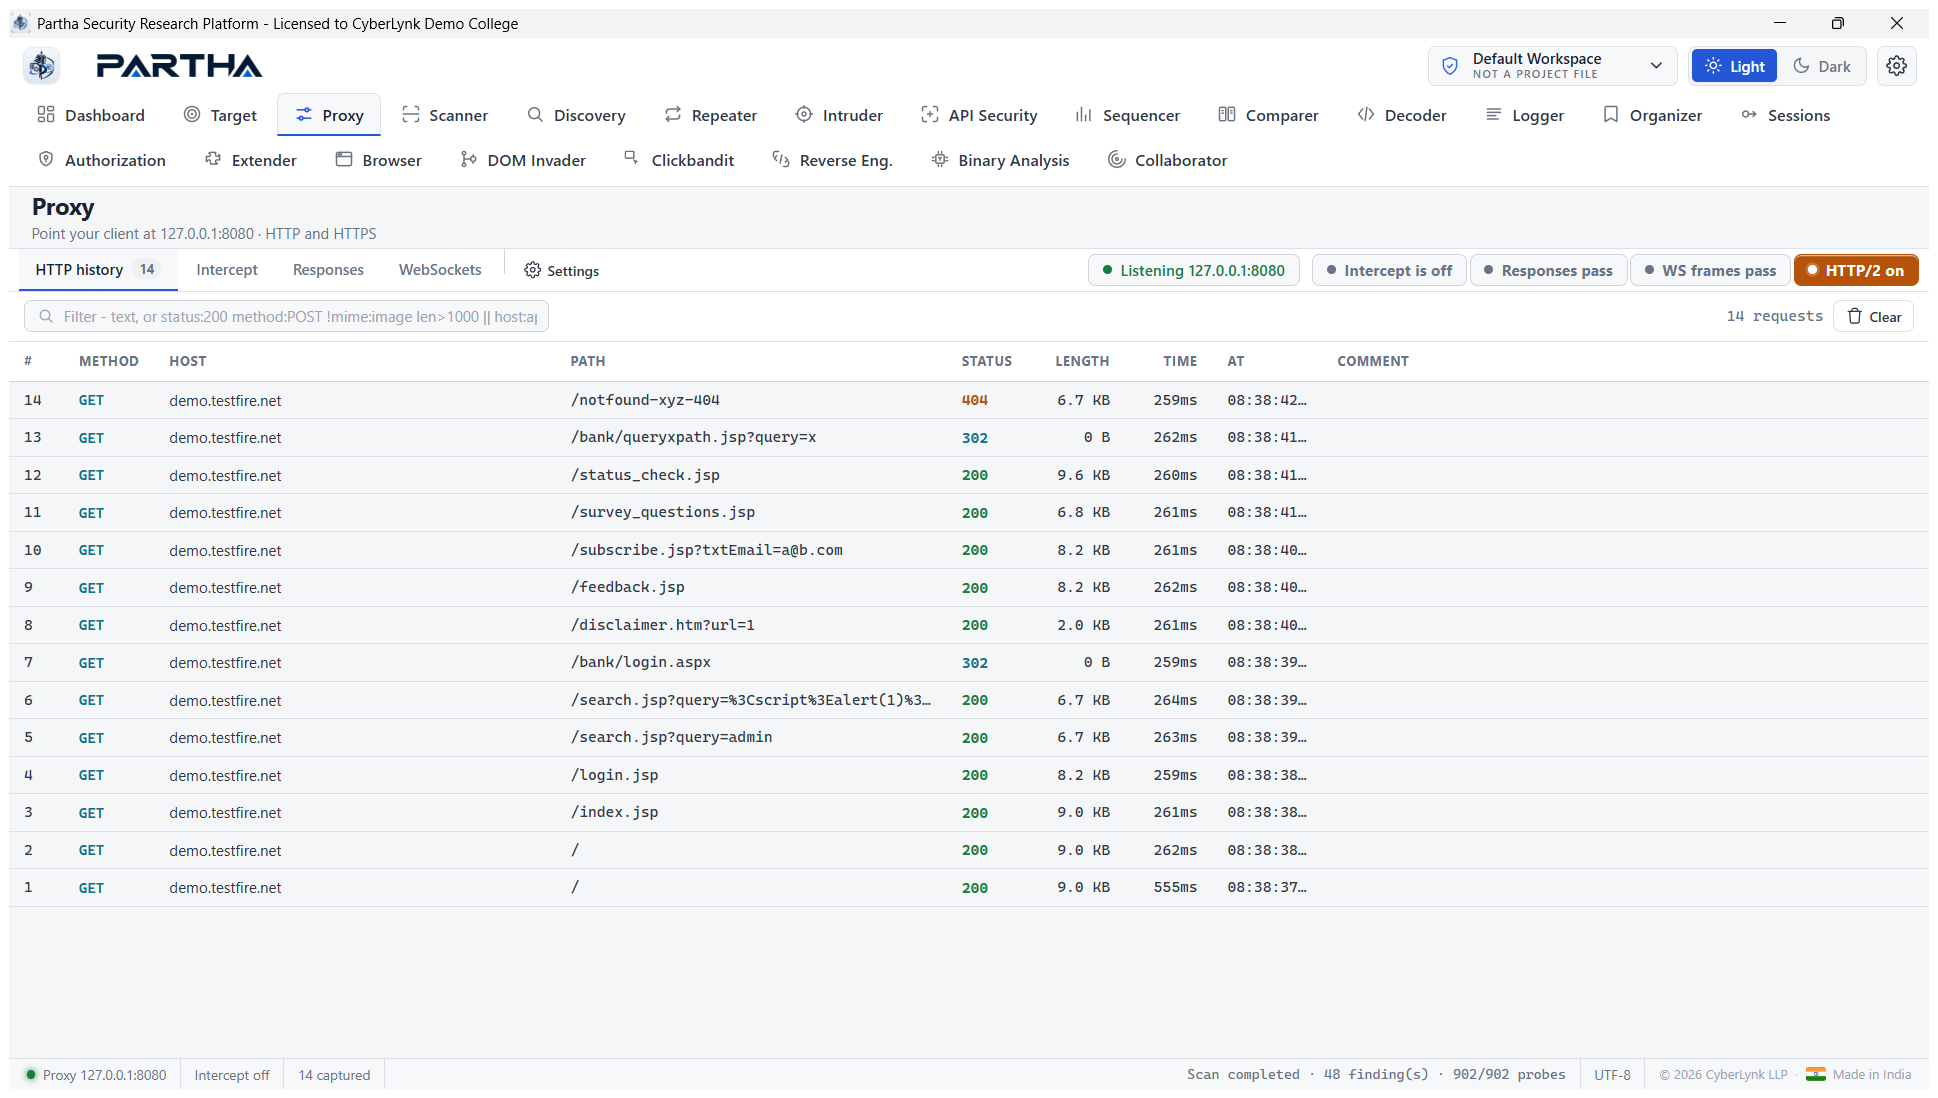
Proxy
Log, intercept and manipulate HTTP, HTTPS and WebSocket traffic, with unrivalled HTTP/2 support and match-and-replace rules.HTTP history — every exchange, with a Bambda-style filter bar.…
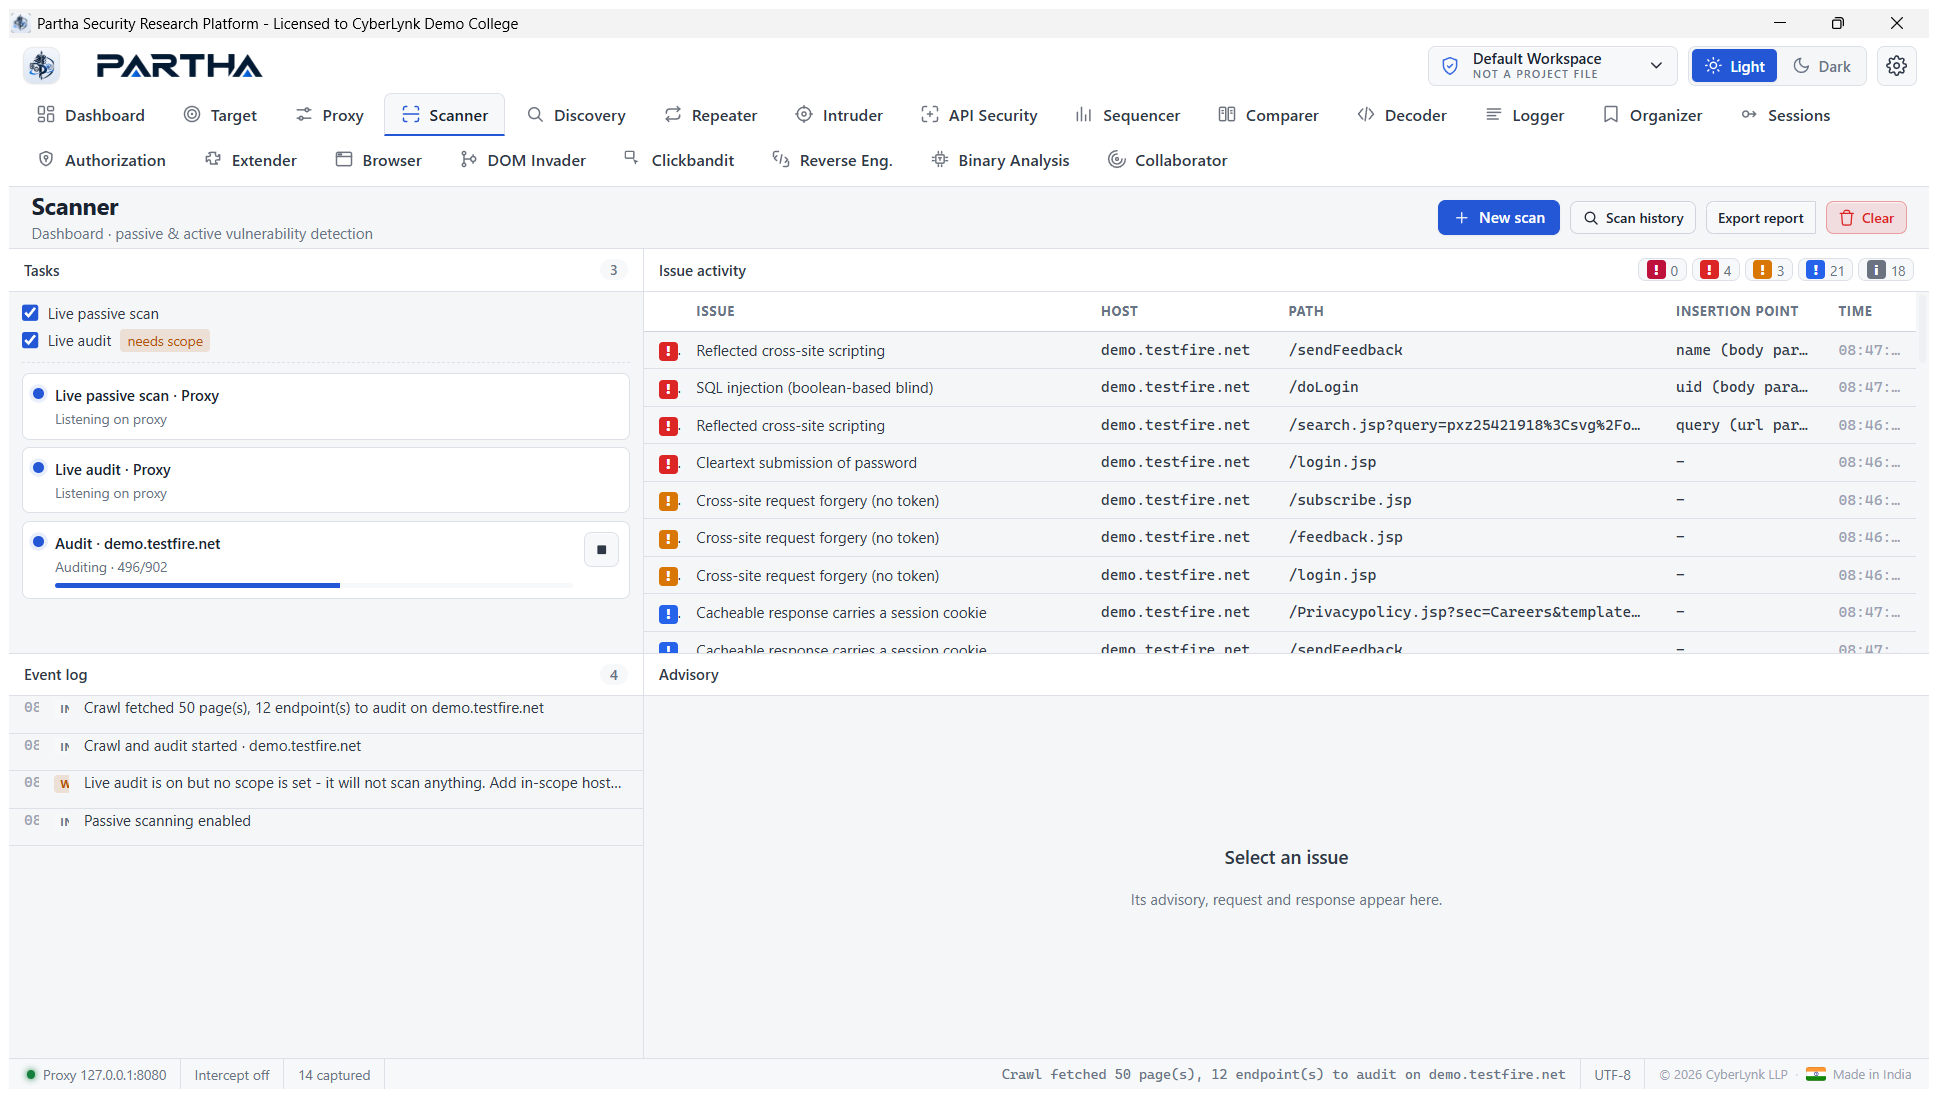
Scanner
Passive scanning as you browse, active auditing of URLs and inputs, and a built-in crawler ("crawl and audit") — optionally through the built-in browser and with authentication.Live…
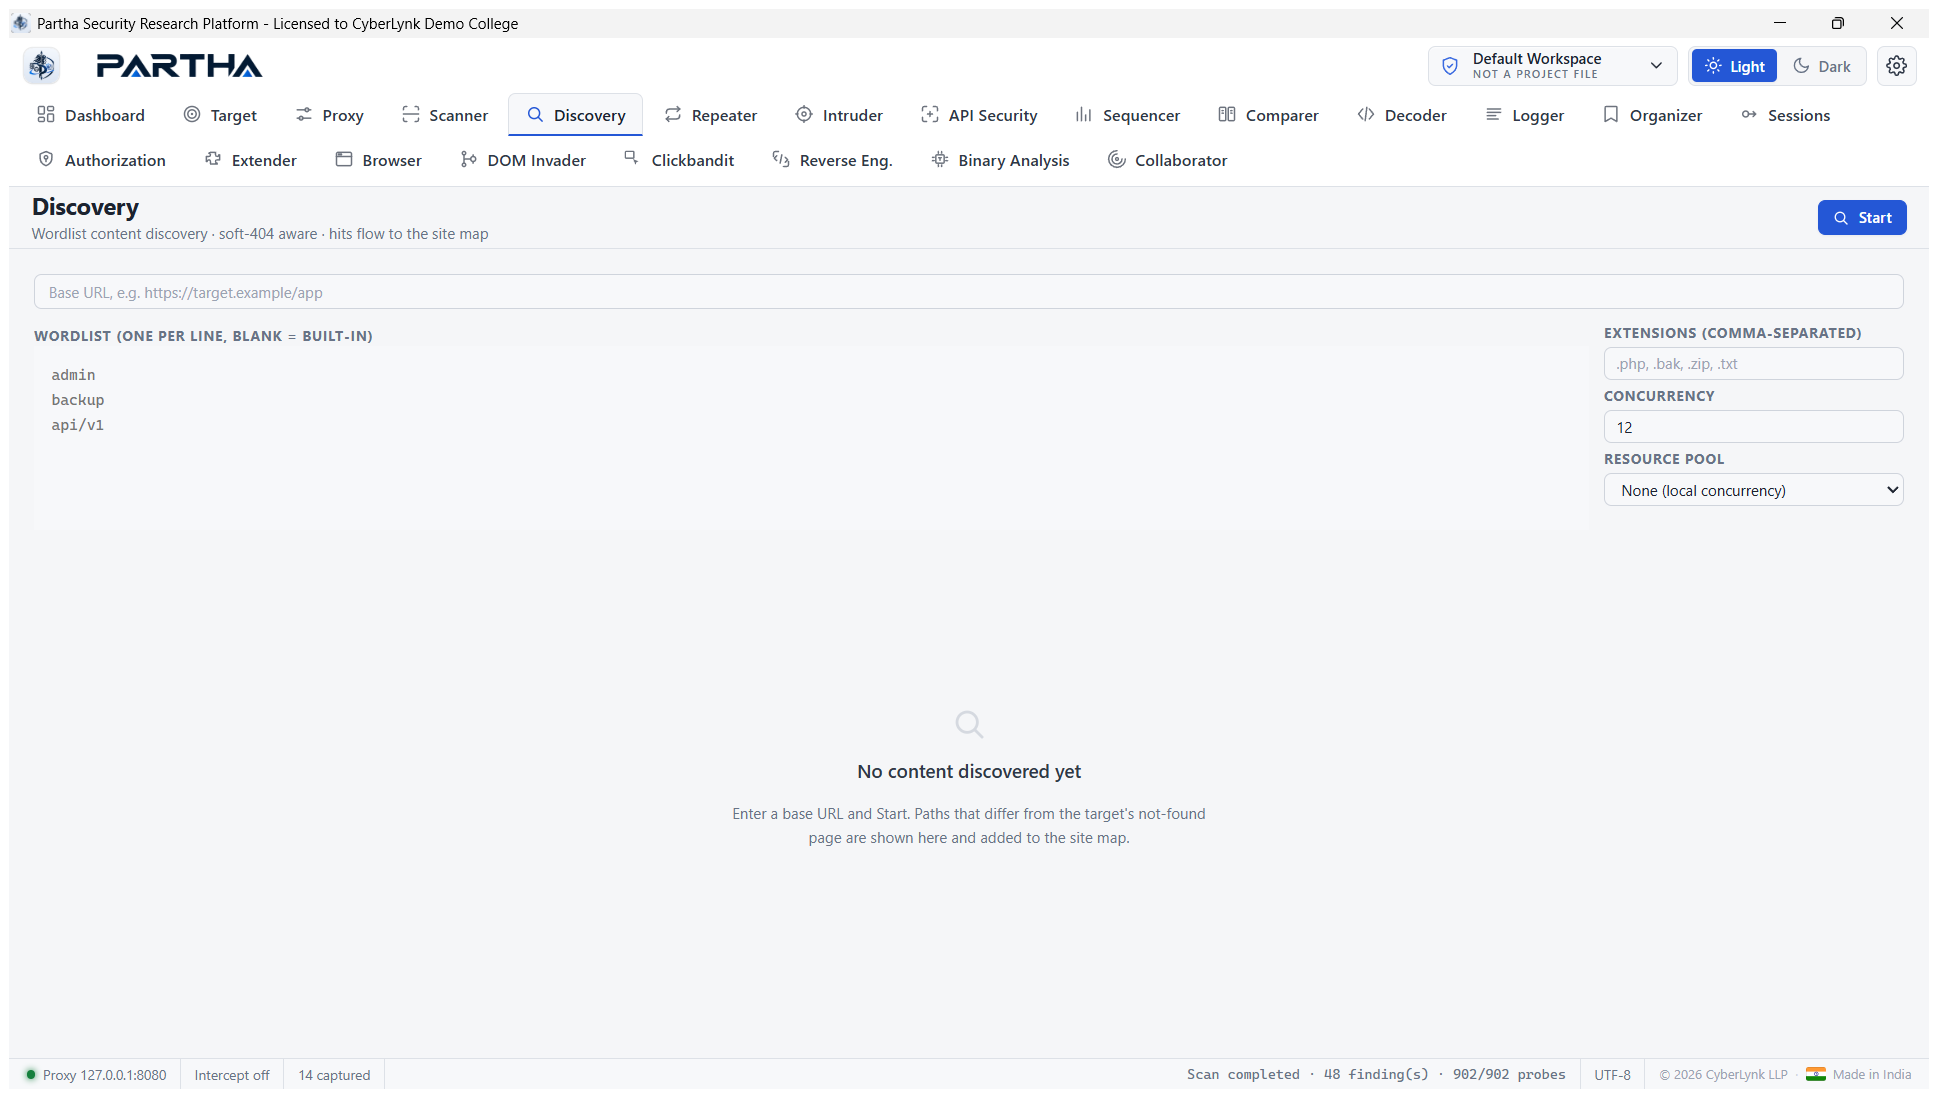
Content Discovery
Expose hidden attack surface by brute-forcing static and dynamic URLs from a wordlist, with soft-404 awareness. Hits flow into HTTP history and the site map.Content DiscoverySteps: enter a…
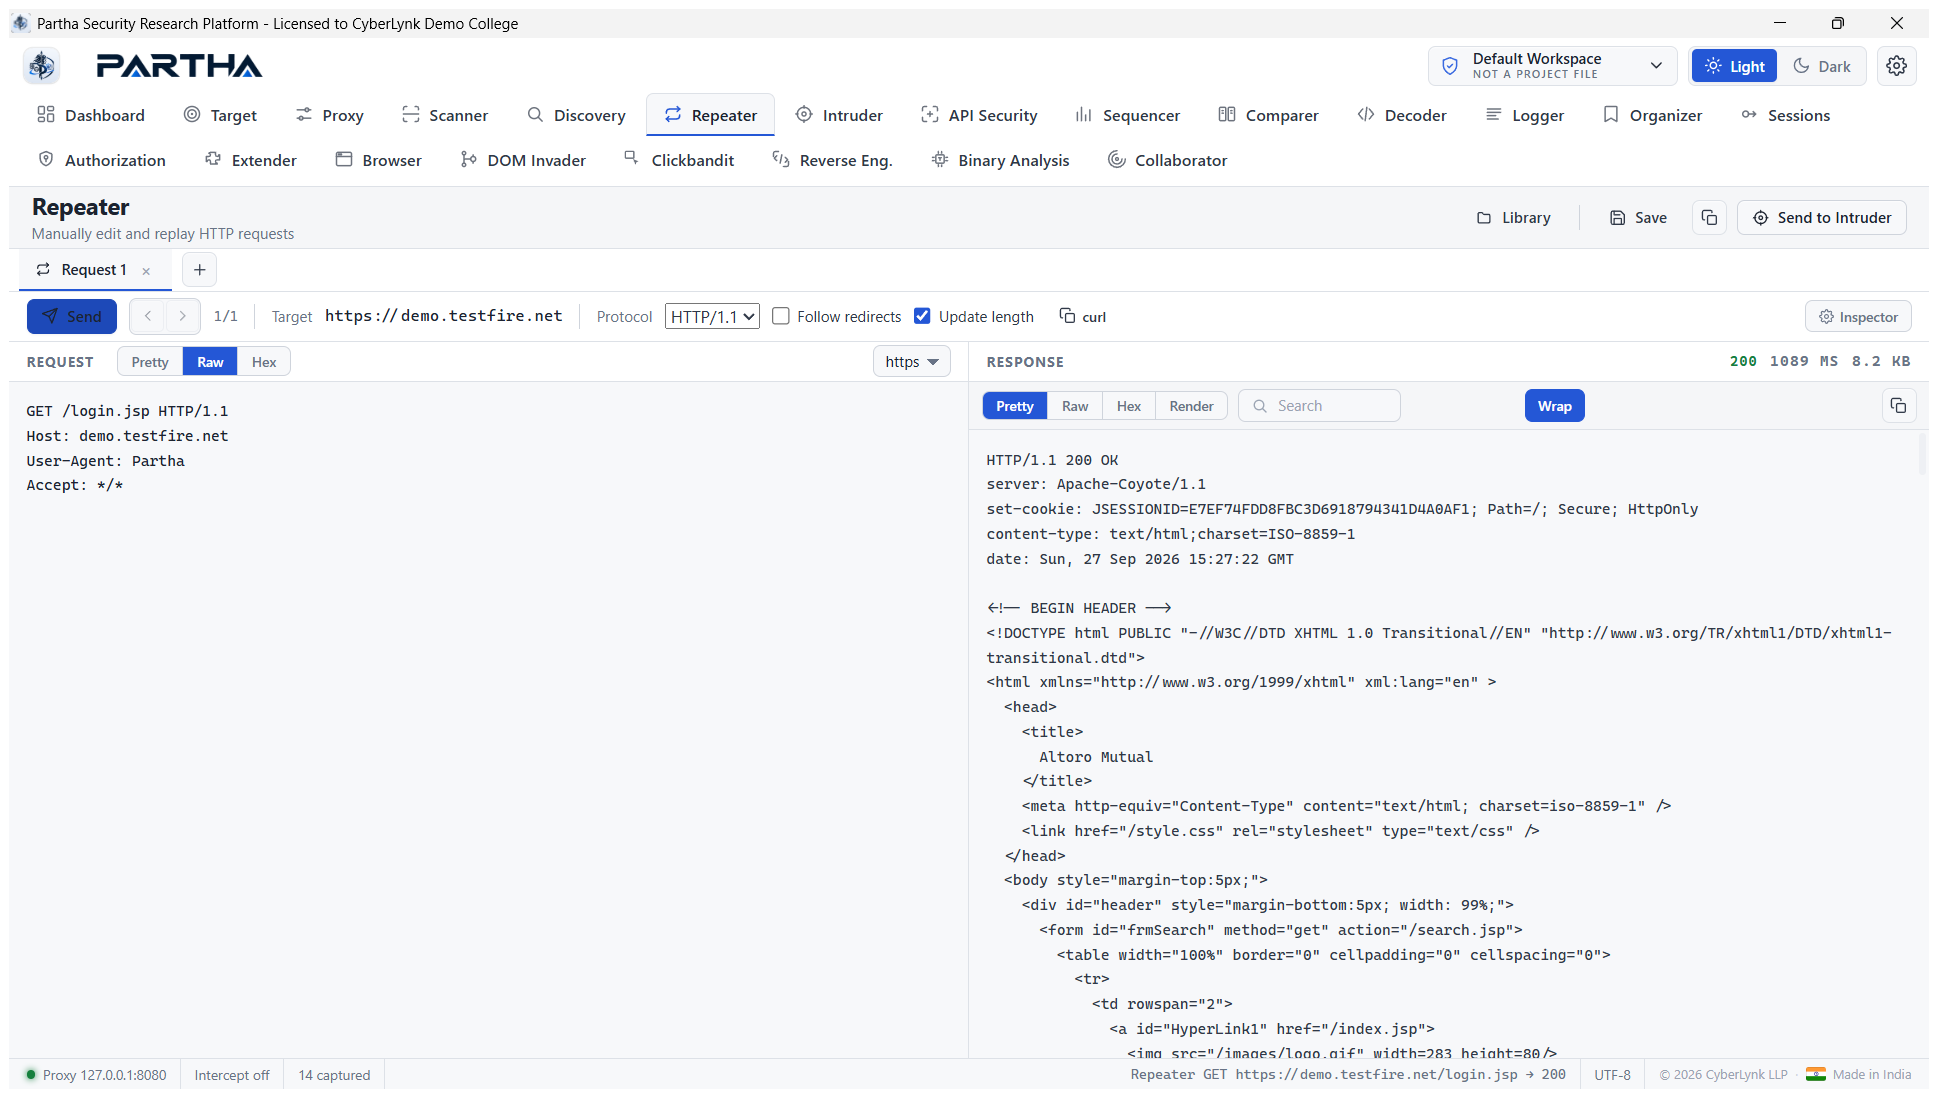
Repeater
The feature-rich HTTP editor — manually edit and replay any request, with tabs, protocol switching, and automatic pretty-printing.A real replay: GET /login.jsp to demo.testfire.net…
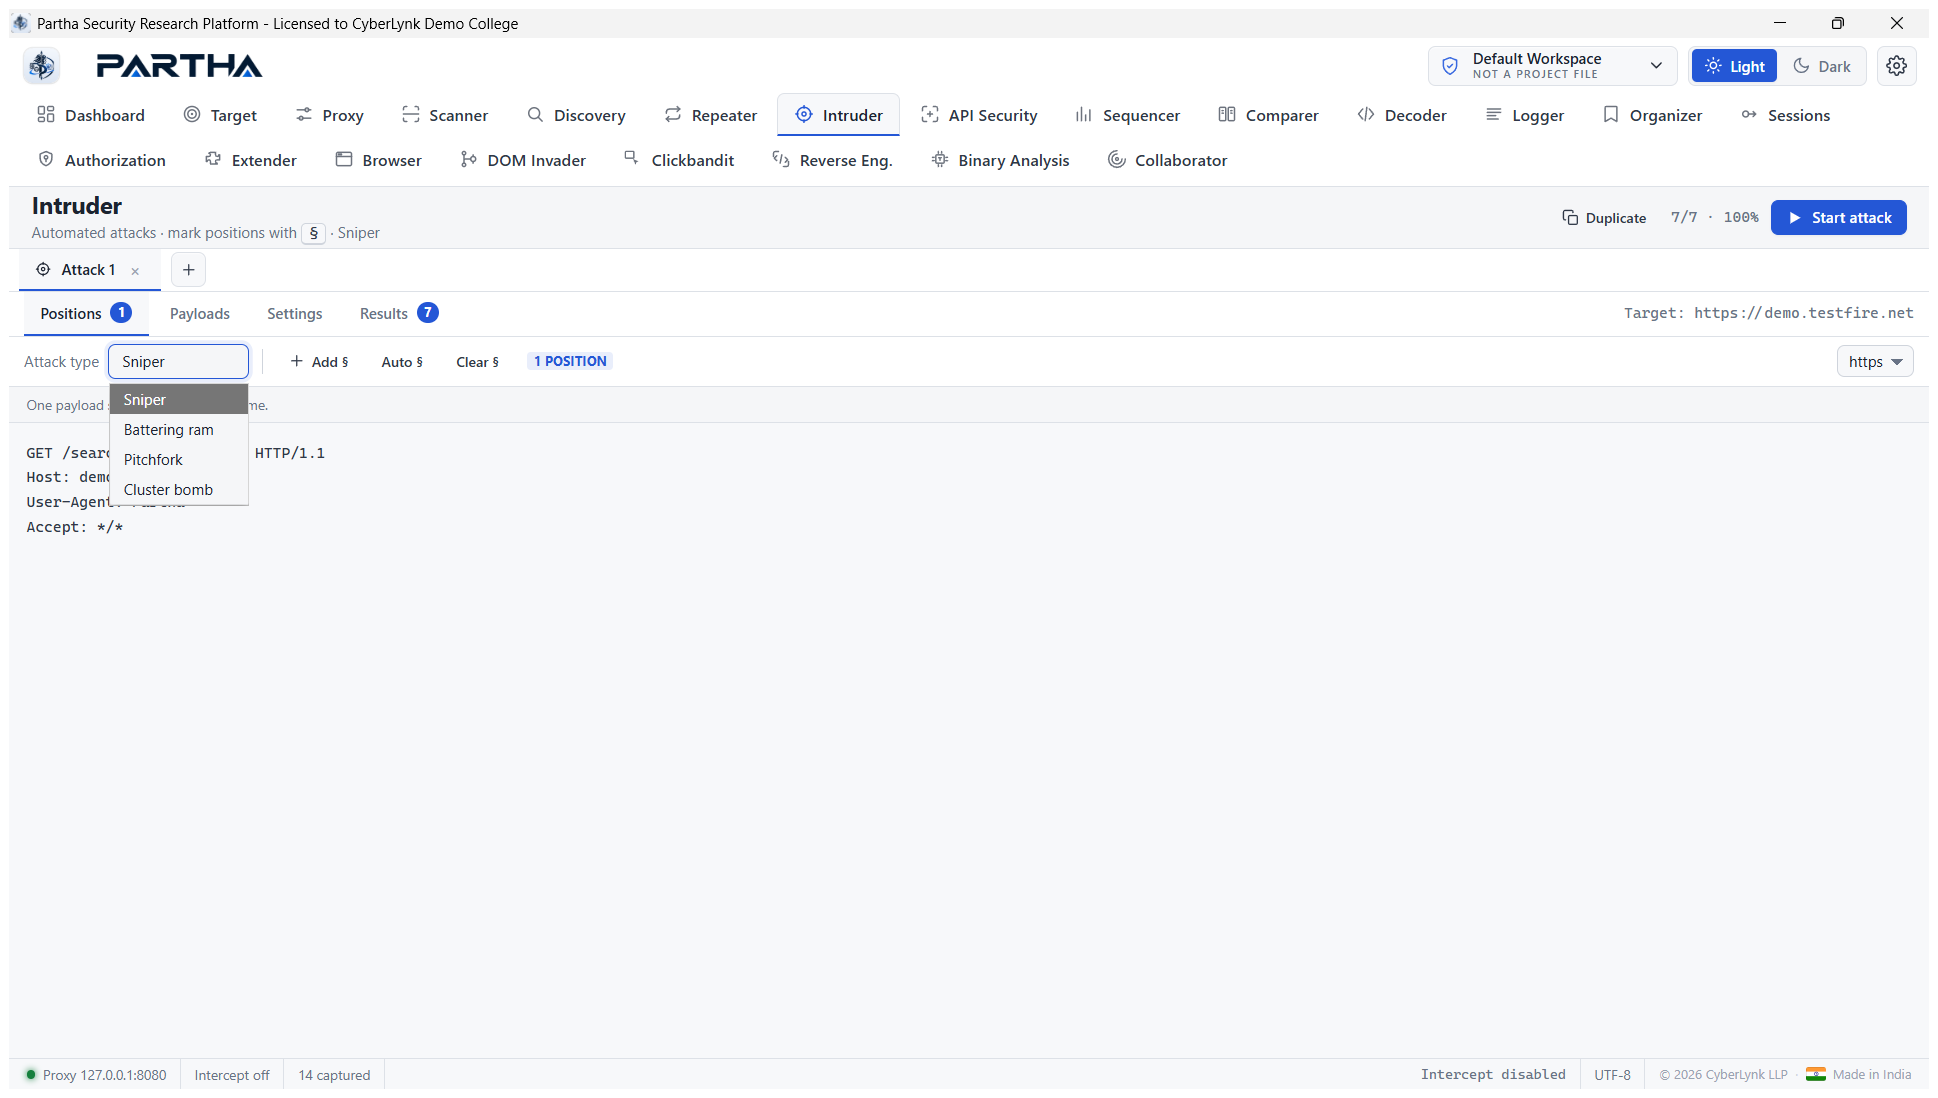
Intruder
Faster brute-forcing and fuzzing with custom payload sets and attack types, and capture / filter / query of results.Positions & payloads — mark injection points with §…§, pick an Attack…
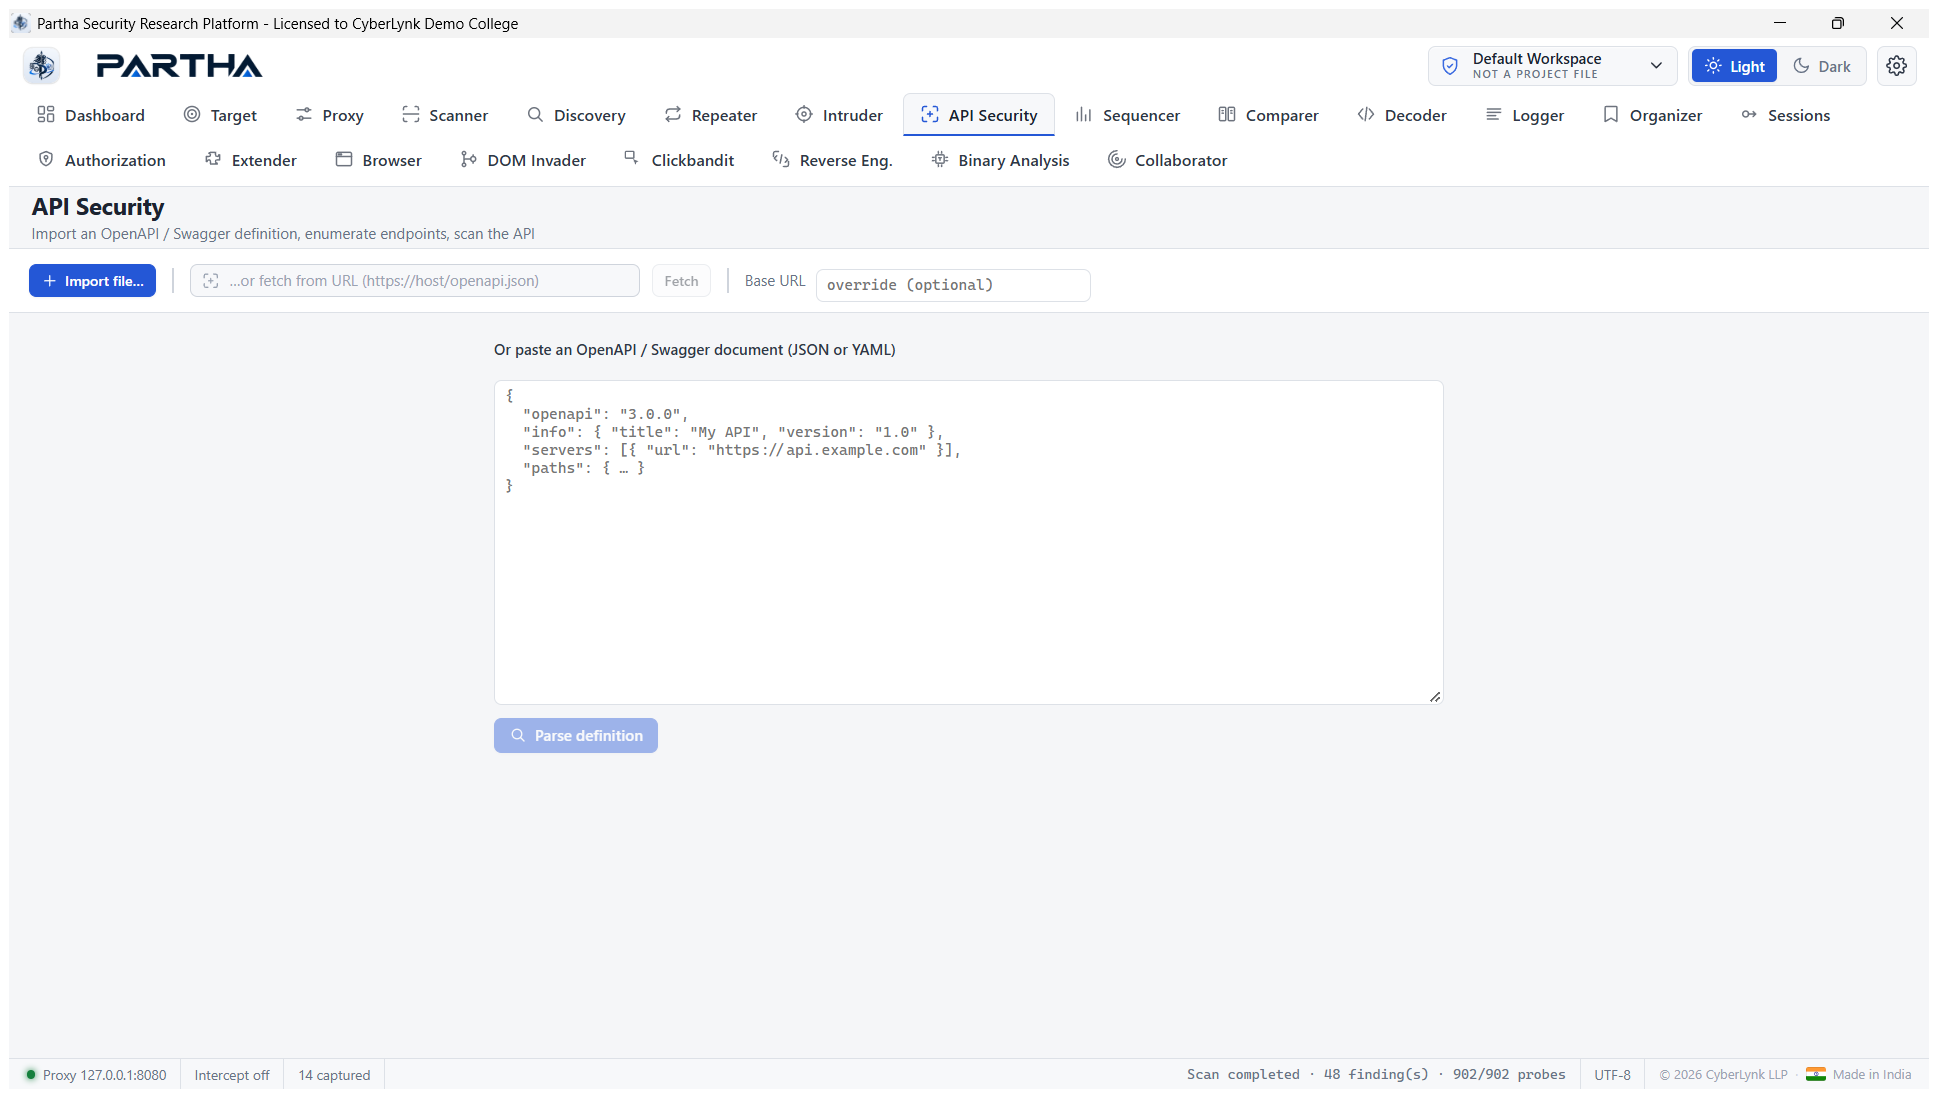
API Security
Scan OpenAPI, GraphQL and SOAP APIs from a definition file. Partha auto-detects the definition kind and enumerates every operation into a ready-to-send request, then runs an API-focused…
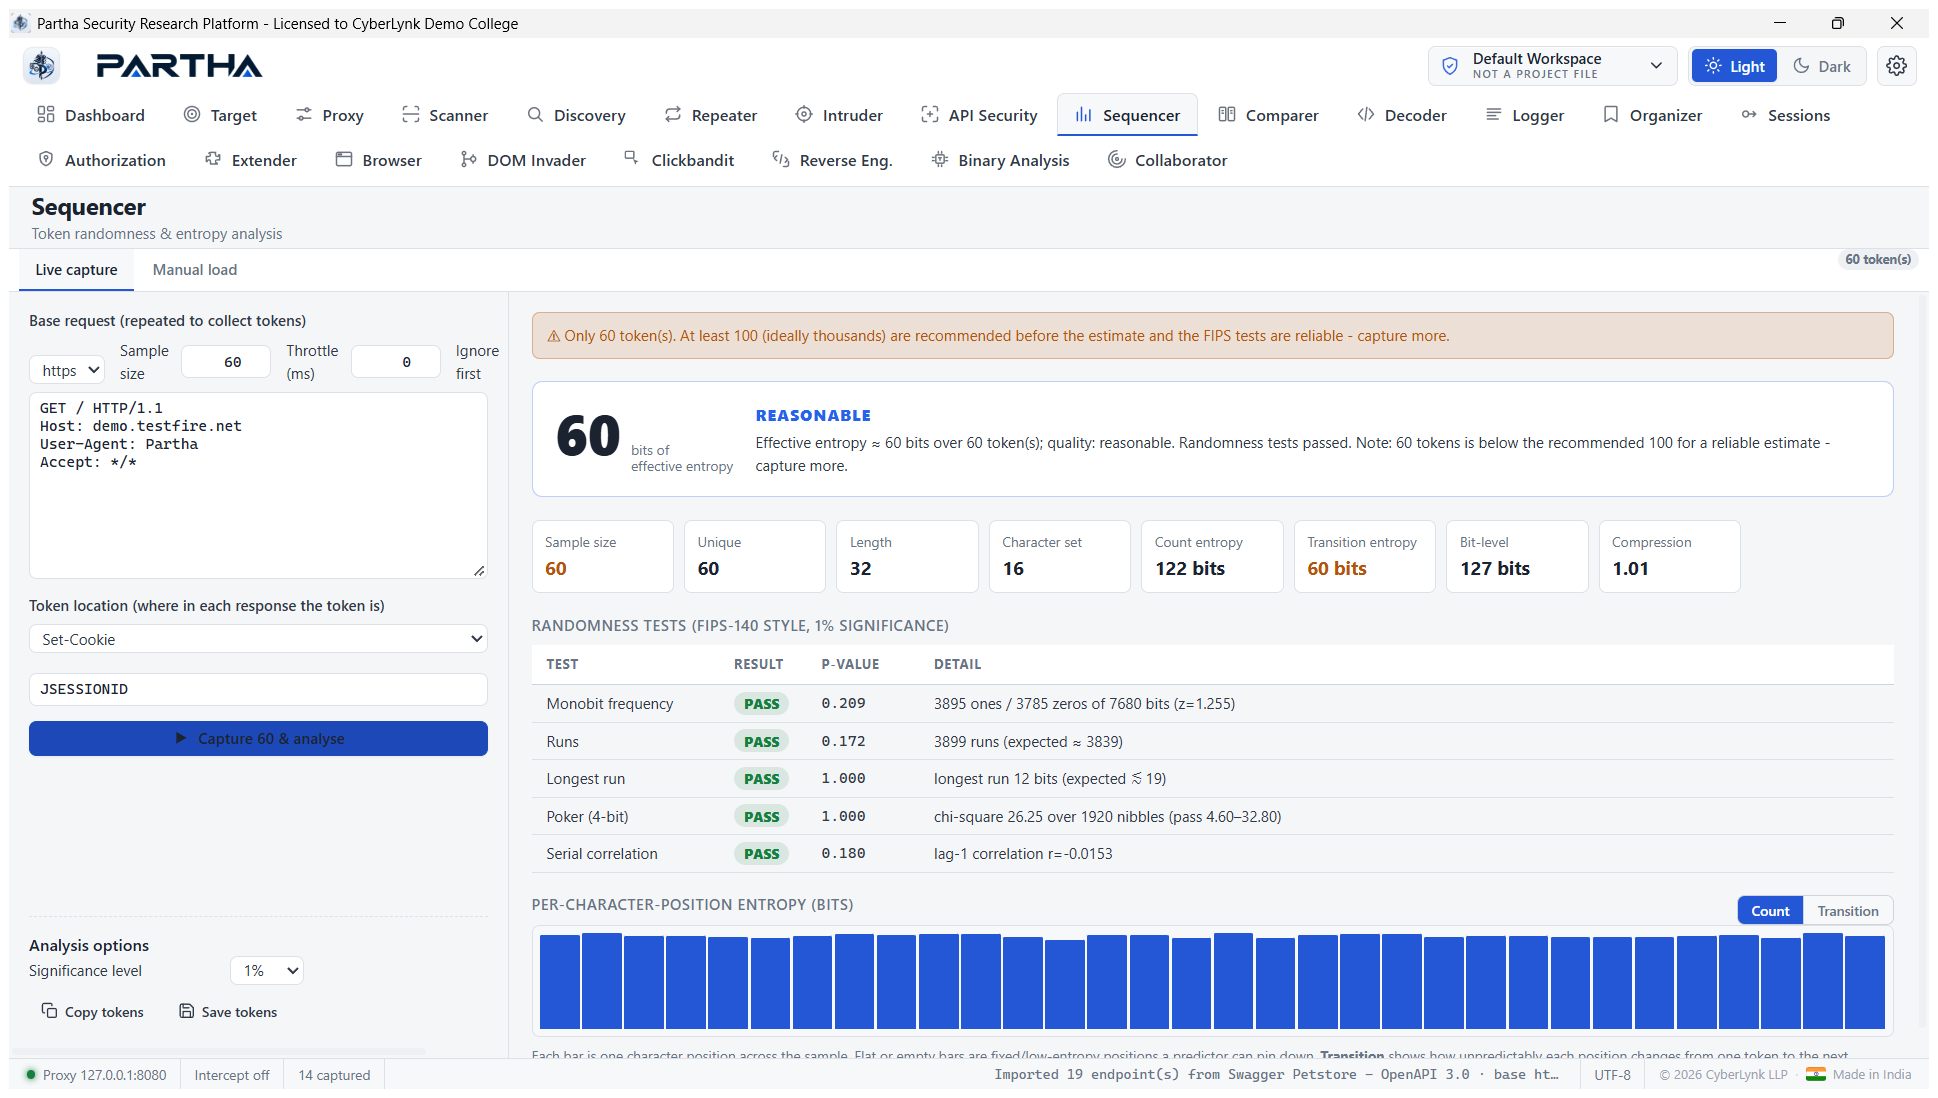
Sequencer
Assess token strength — test the quality of randomness in session tokens.Real result — capturing 60 JSESSIONID cookies from demo.testfire.net yielded ≈60 bits of effective entropy…
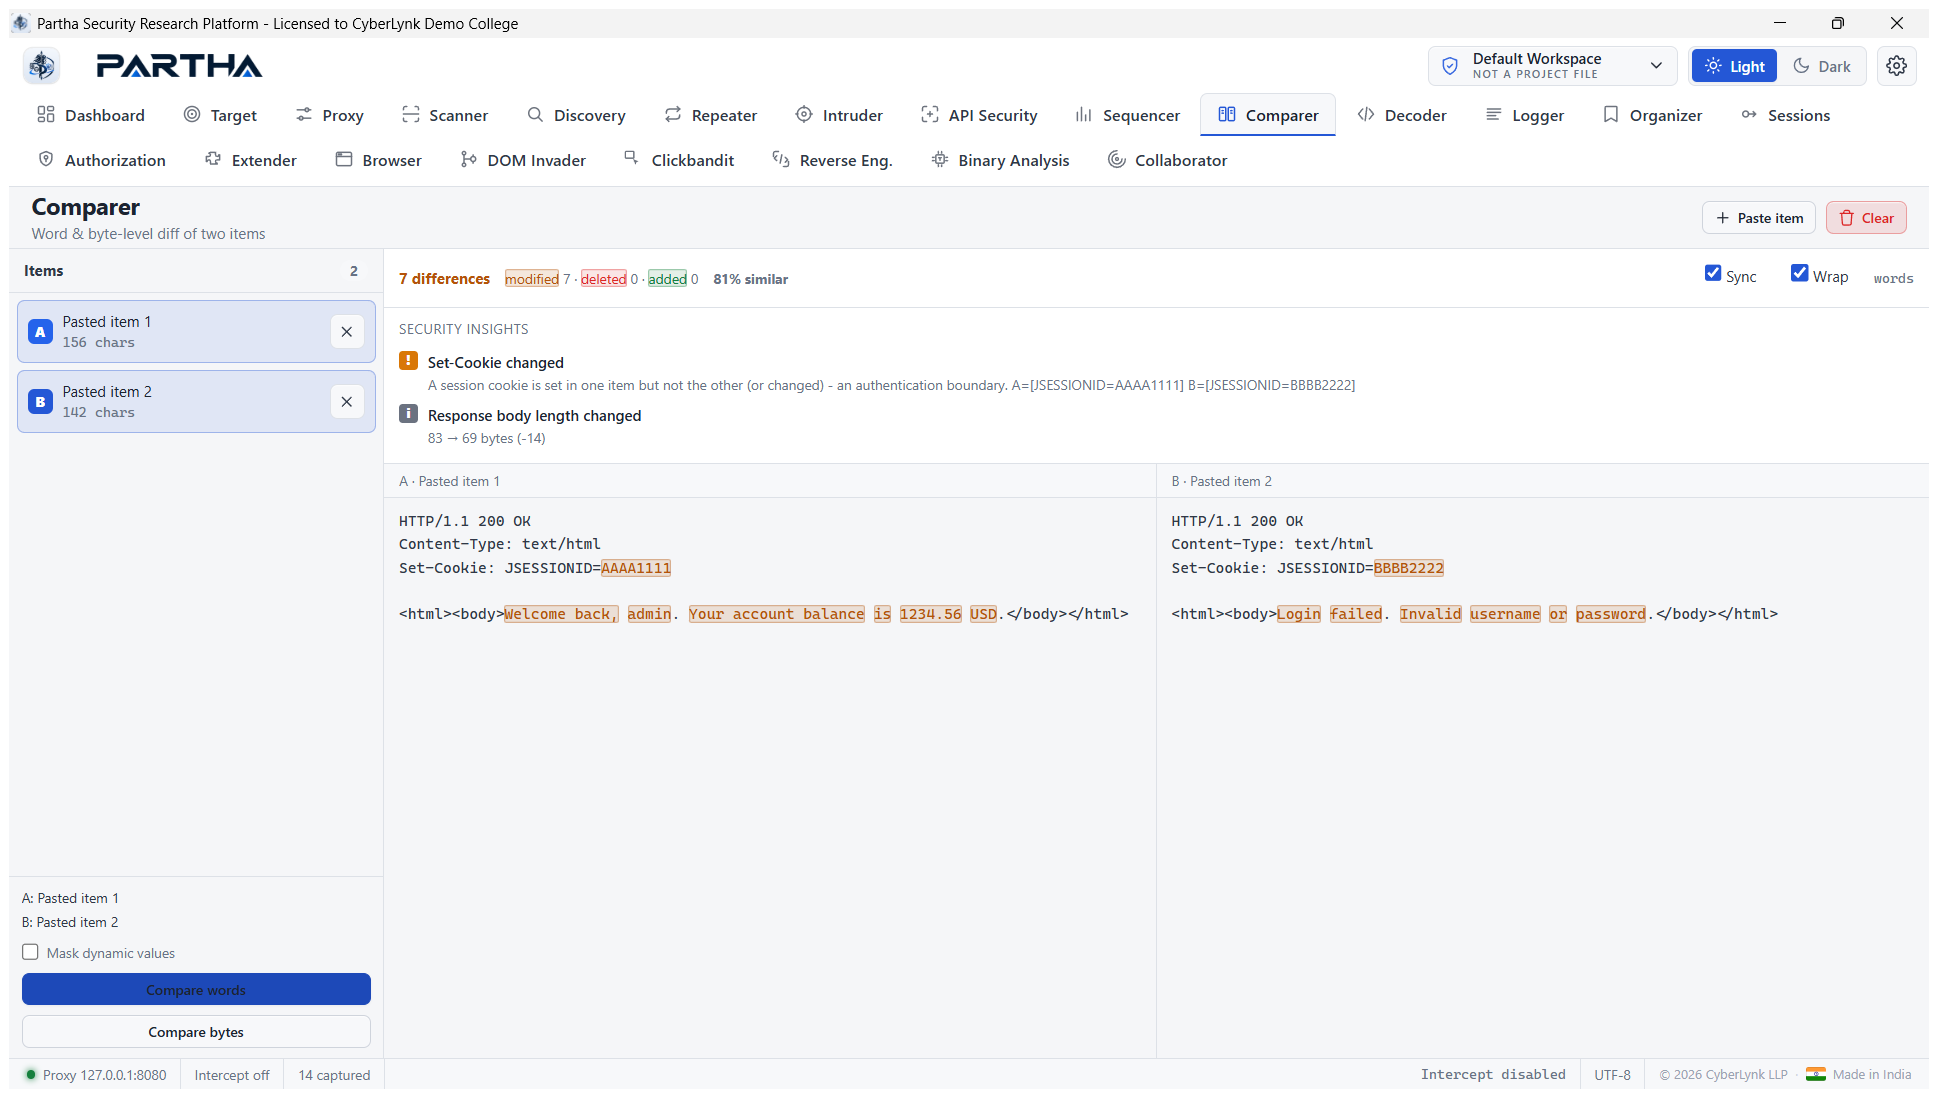
Comparer
Word- and byte-level diff of two items, with security insights.Real result — diffing two HTTP responses shows 7 differences, 81% similar, with Security Insights flagging the Set-Cookie…
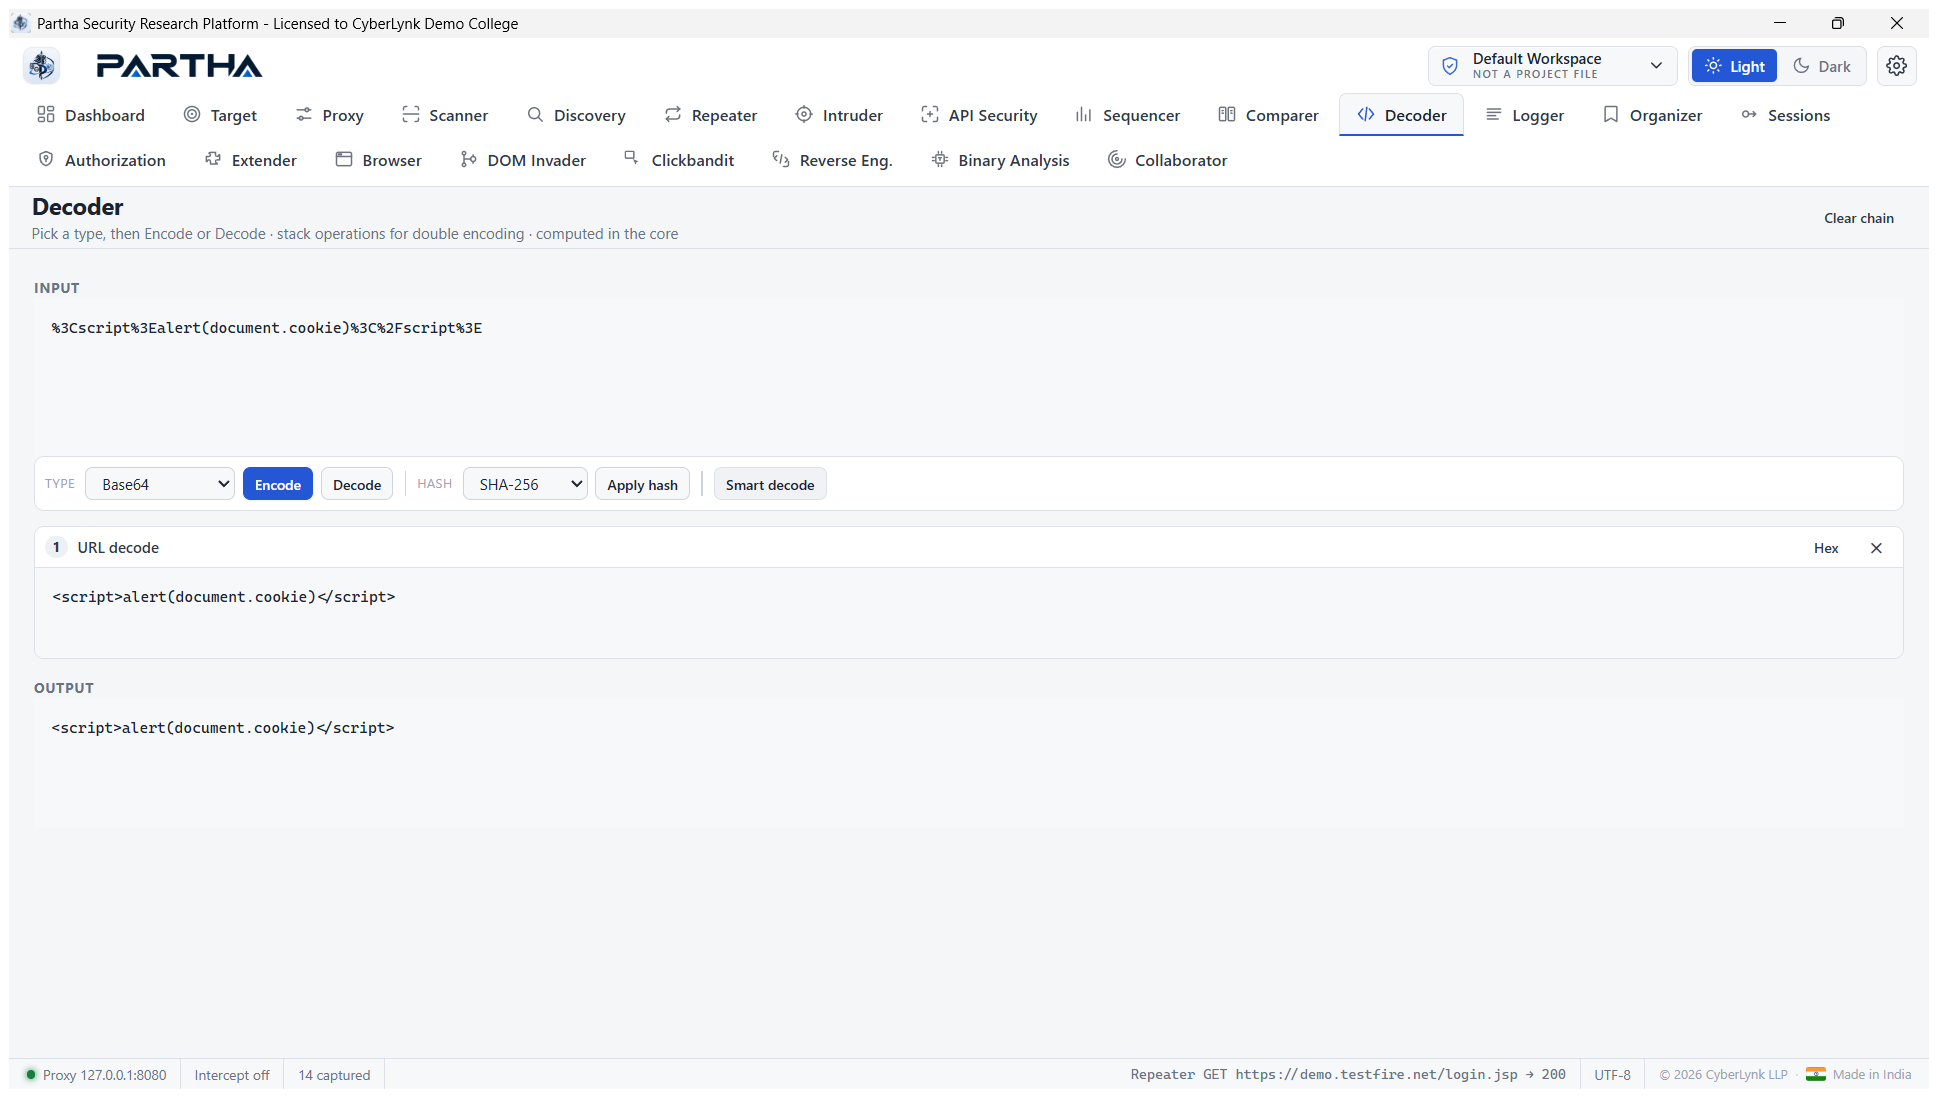
Decoder
Transform data with a stackable chain of encoders/decoders and hashes.Real result — Smart decode on the URL-encoded XSS payload seen on the target…
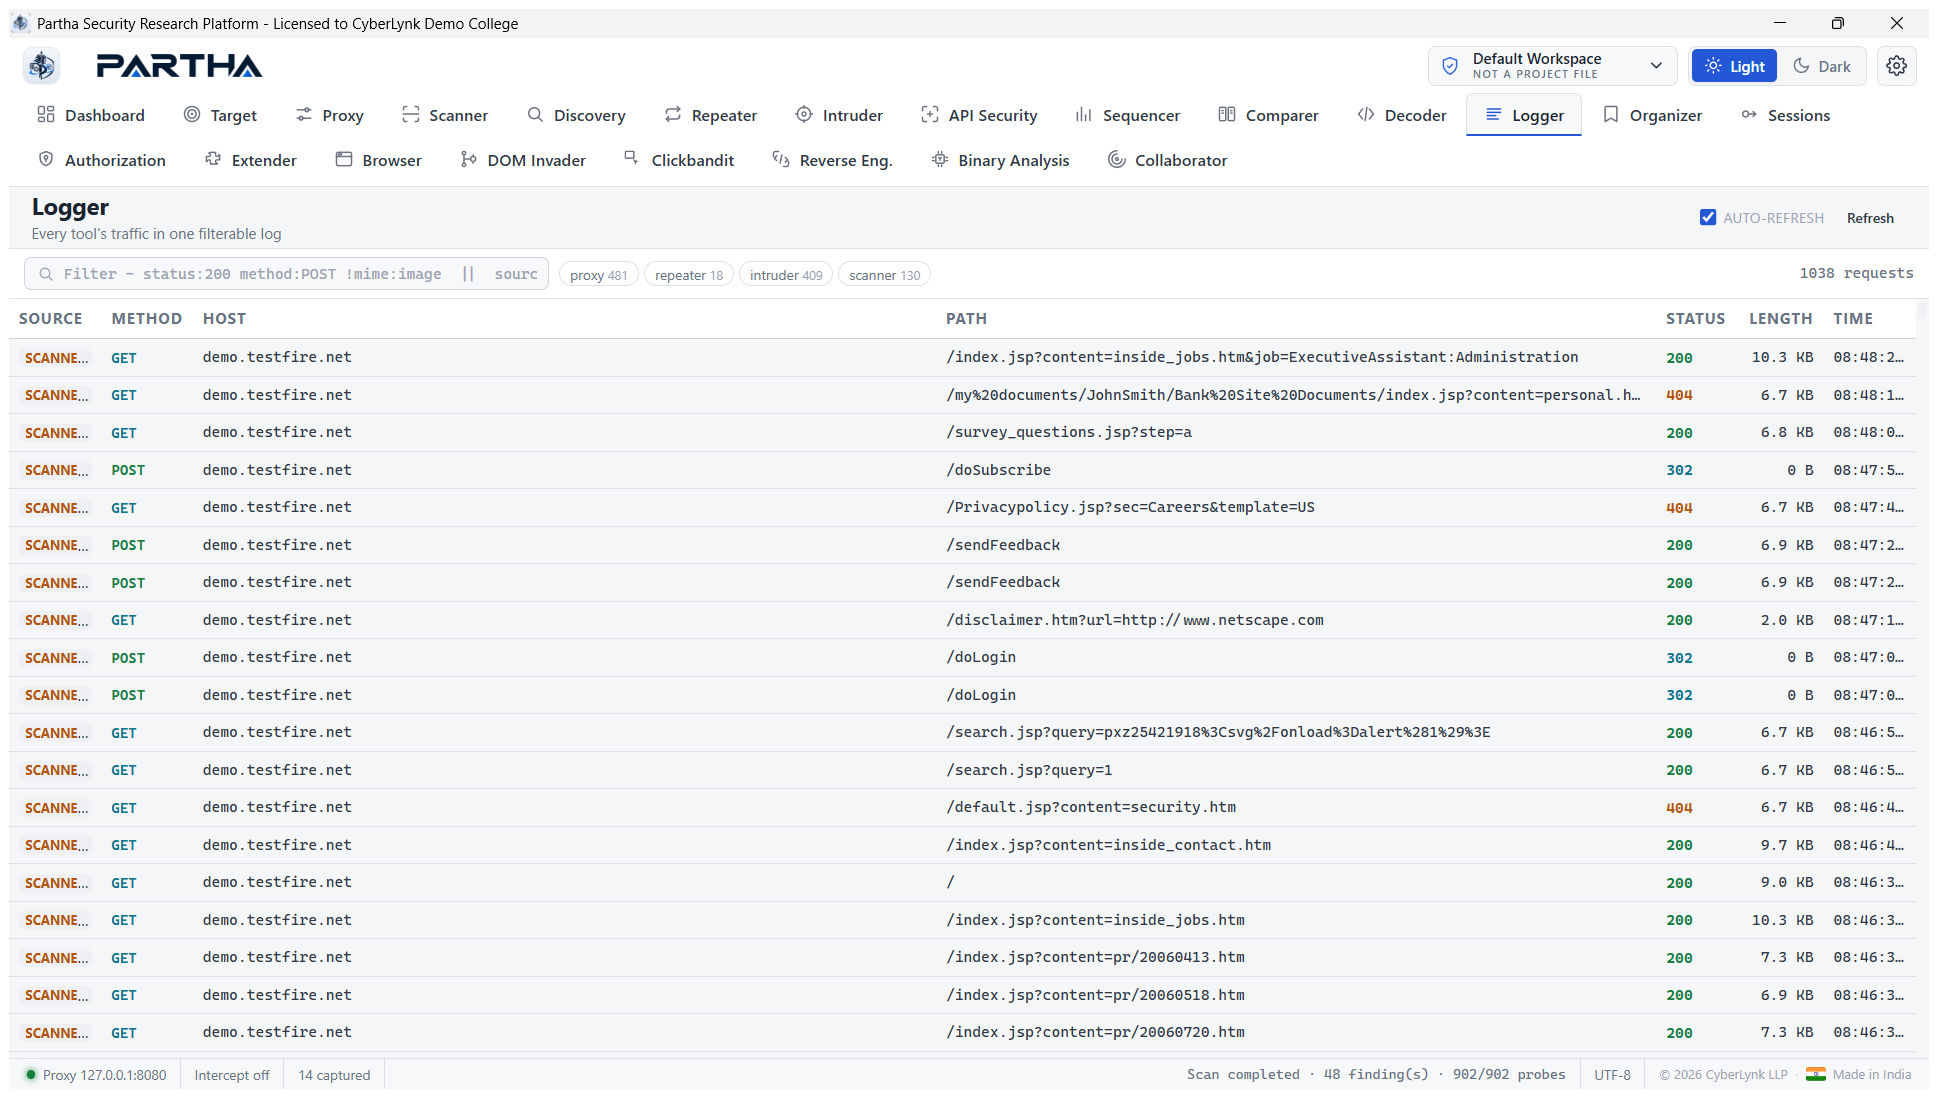
Logger
Every tool's traffic in one filterable, sortable, searchable log, each row tagged with its source (Proxy / Repeater / Intruder / Scanner / Crawler).Logger — all trafficReal result —…
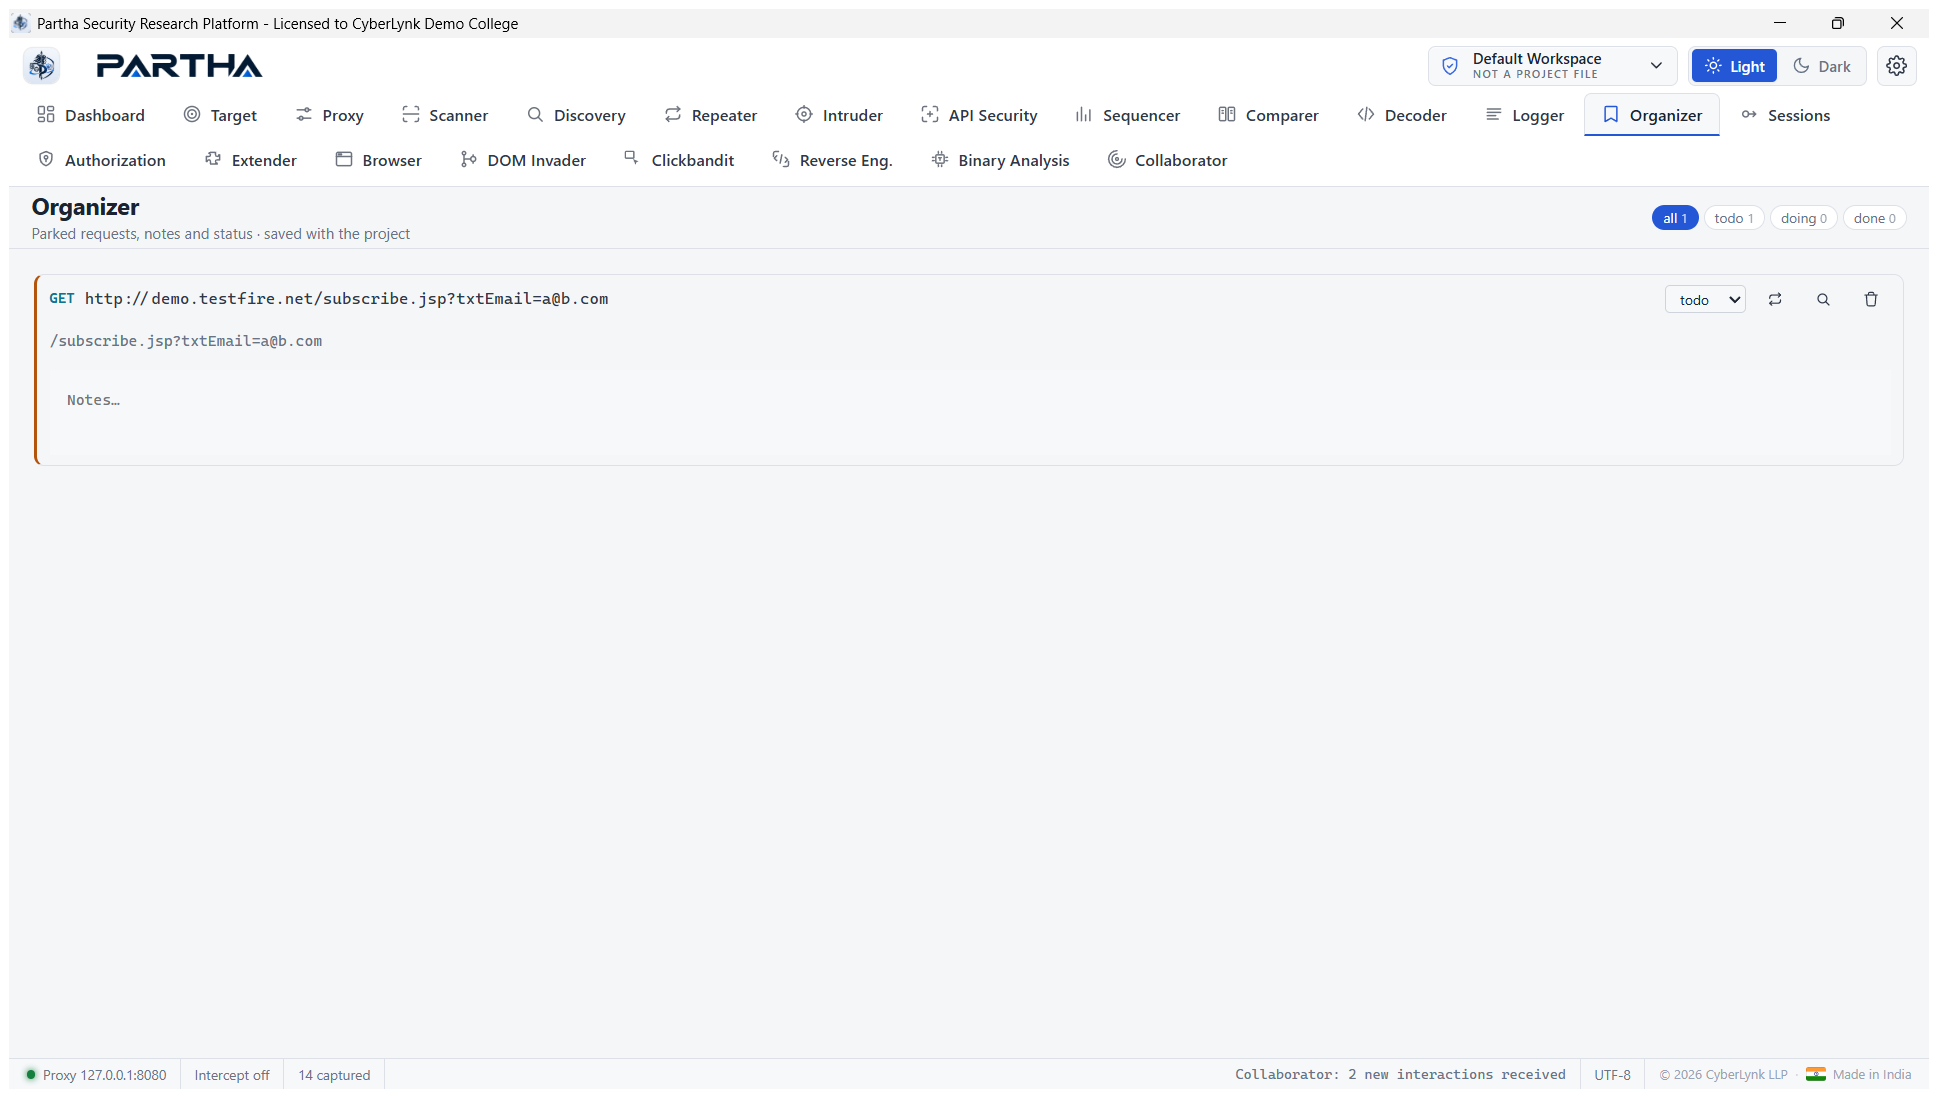
Organizer
Store and annotate interesting messages — park any request with a note and a workflow status.Real result — a testfire request parked from the Proxy context menu, shown with a todo status…
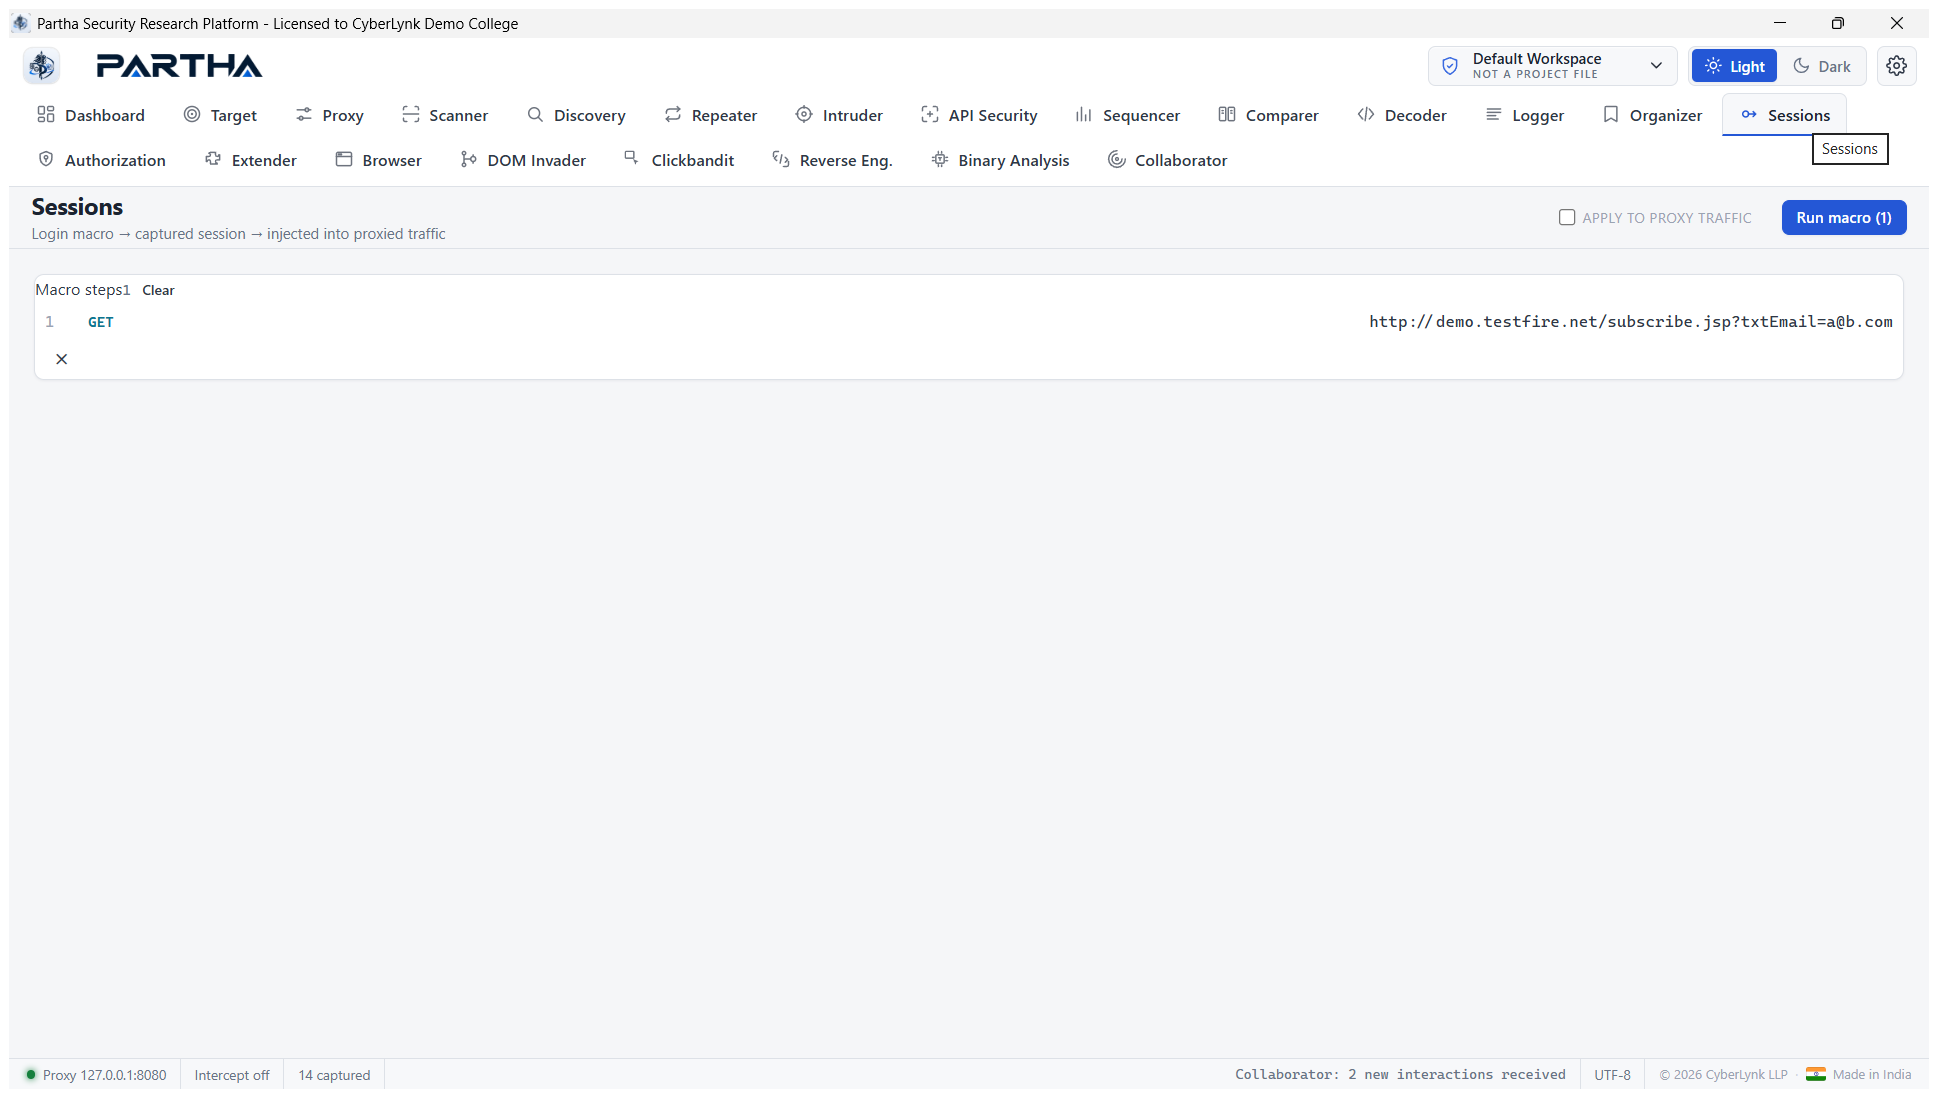
Sessions
Authenticated testing via a login macro whose captured session is injected into proxied traffic.Real result — a testfire request added as macro step 1 via the Proxy context menu; Run macro…
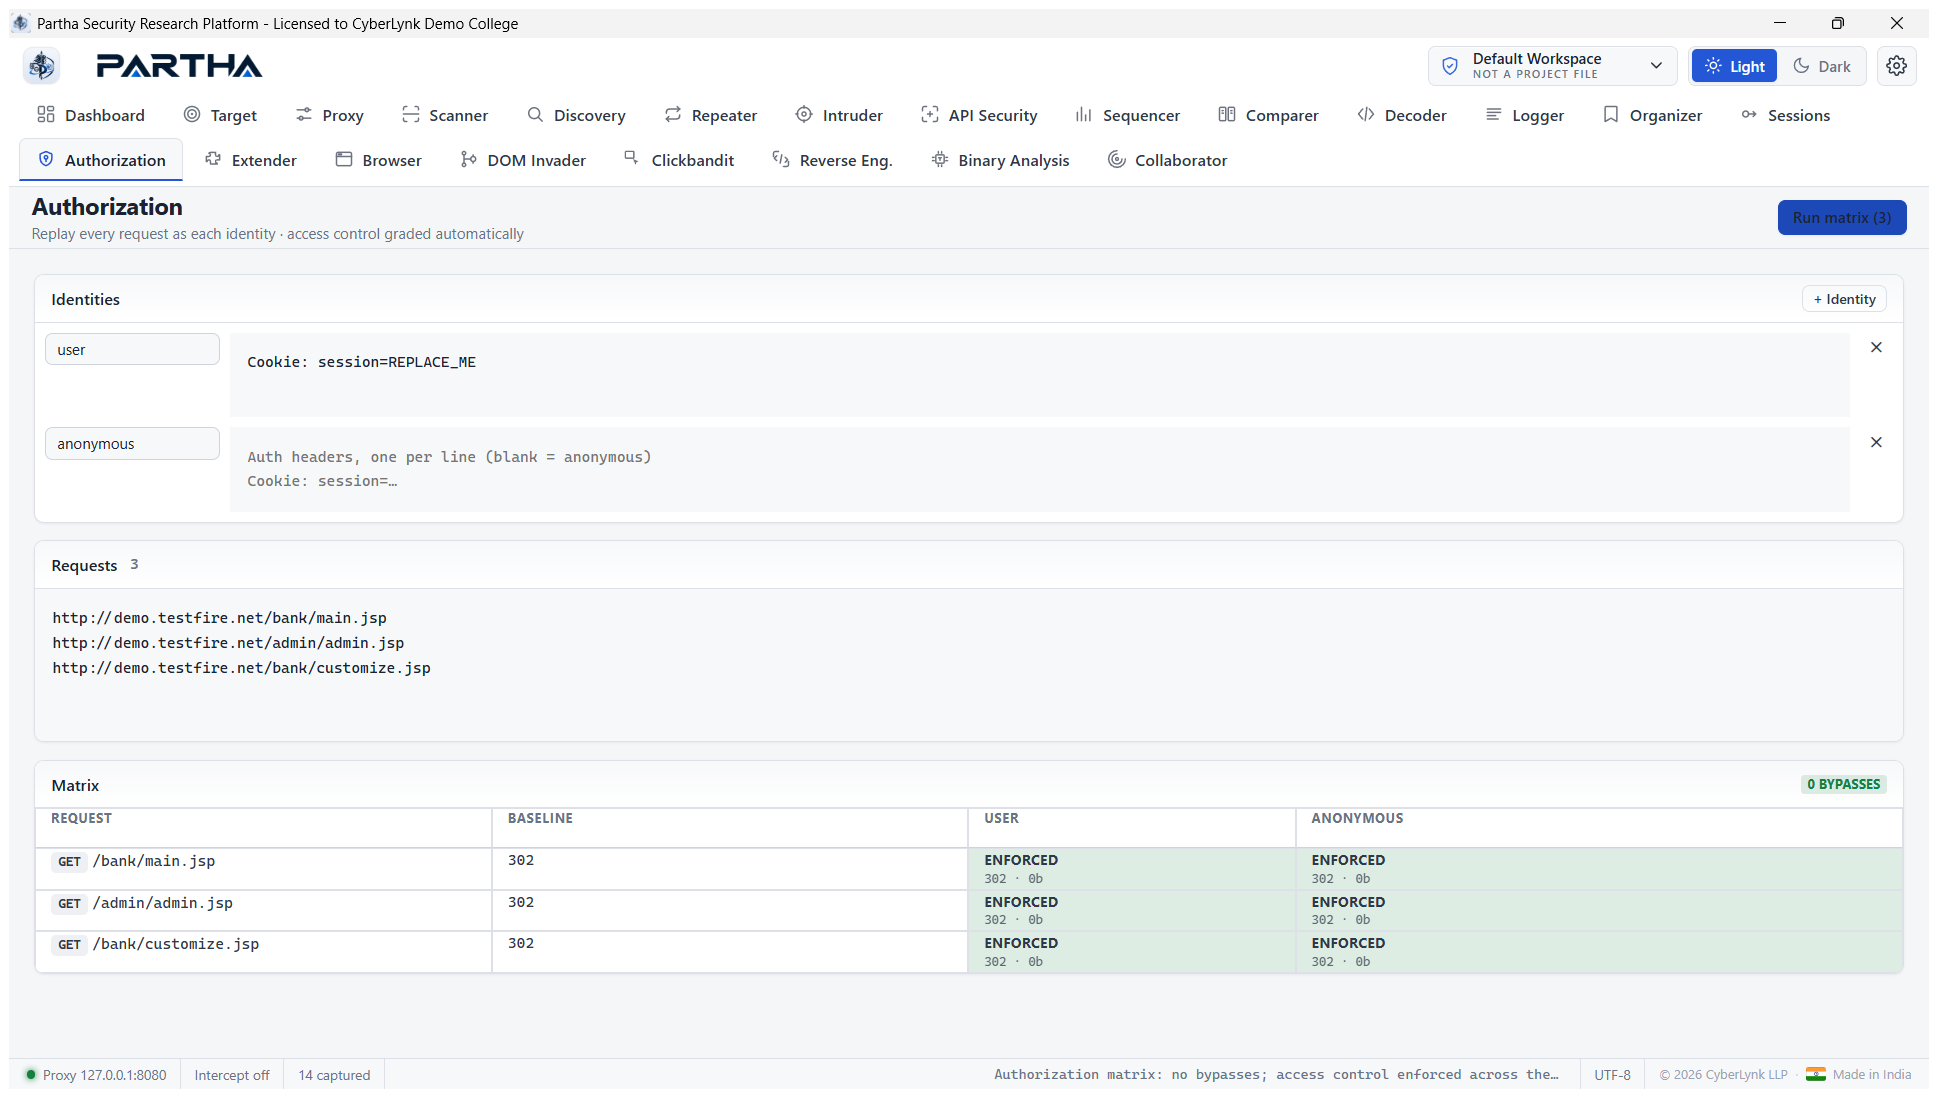
Authorization
Access-control testing — replay every request as each identity and grade the result automatically (a broken-access-control matrix).Real result — three protected testfire URLs replayed as…
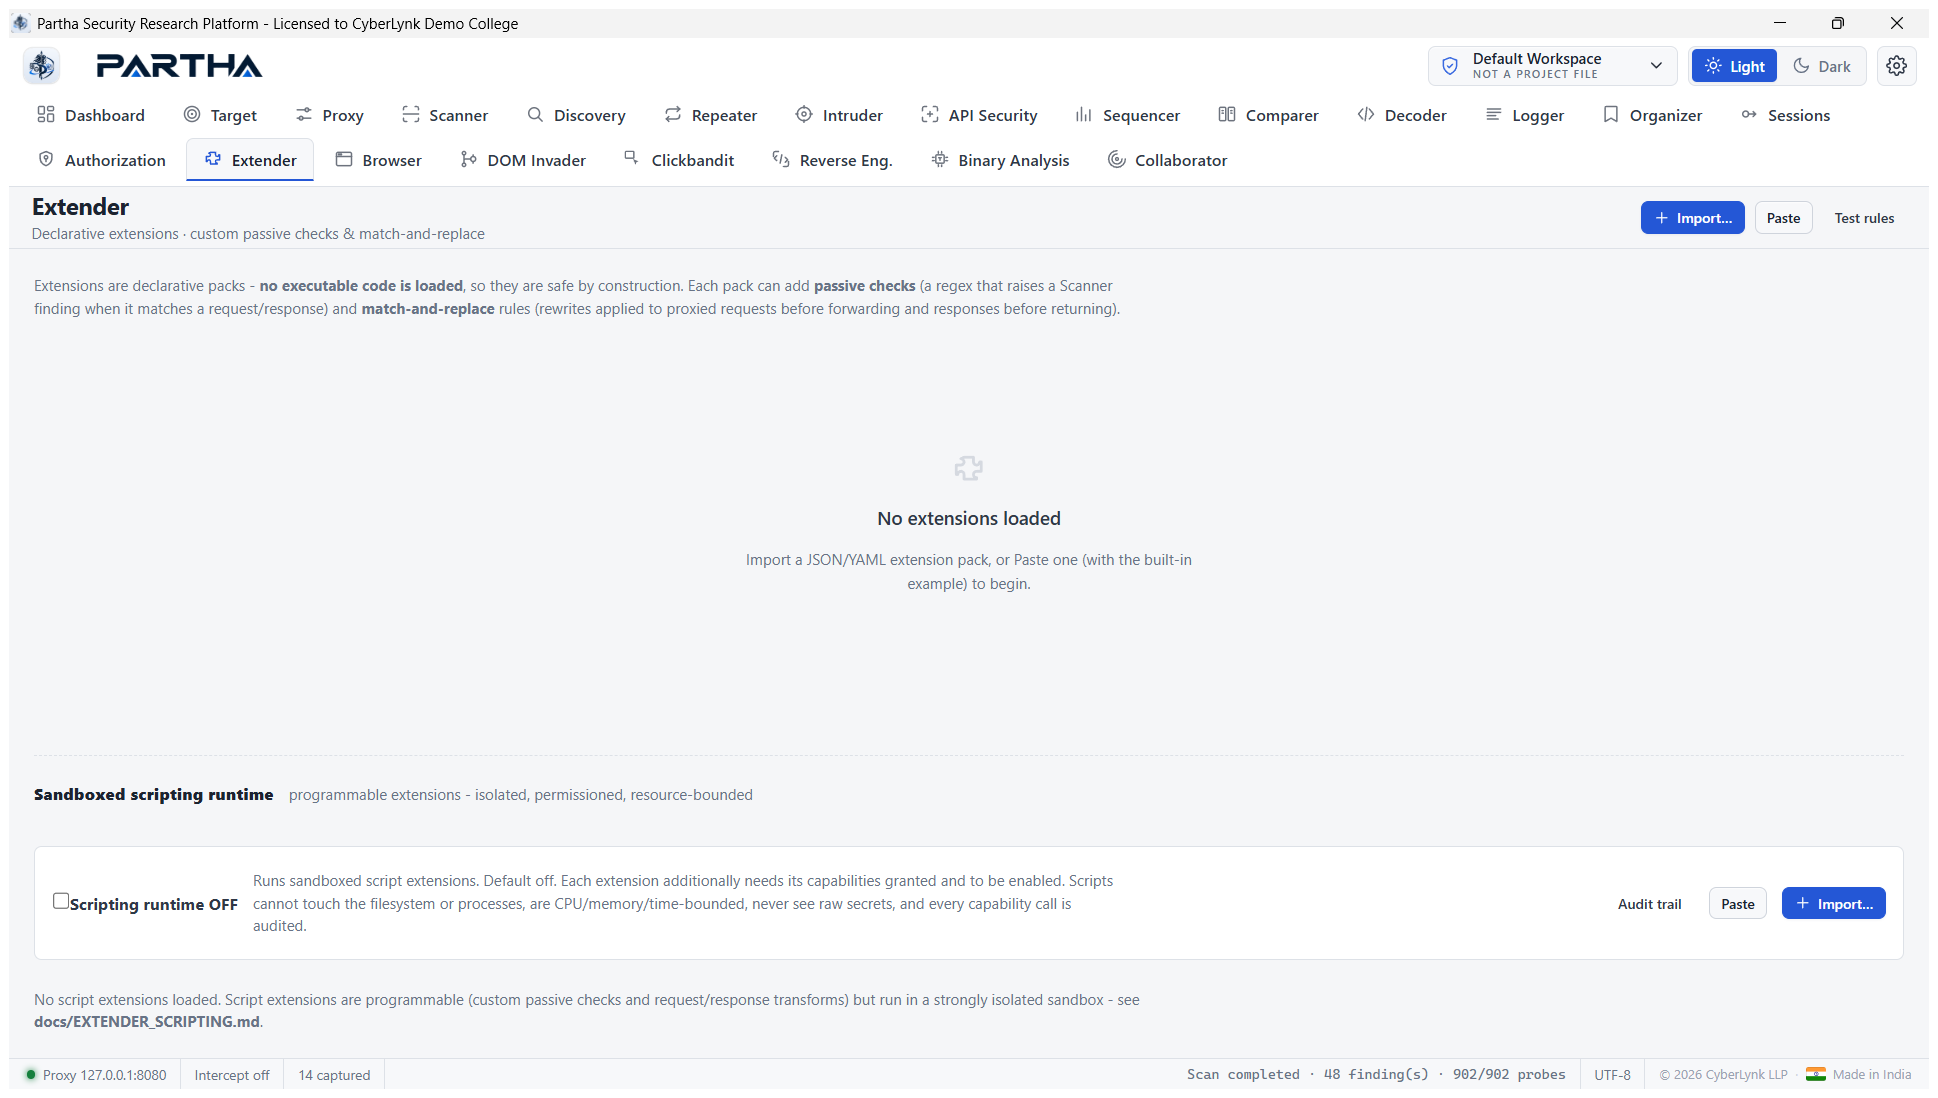
Extender — add-on module
The extensibility / add-on module — extend Partha with declarative packs and a sandboxed scripting runtime, safe by construction.ExtenderComposing a pack — Paste (or Import) a Partha…
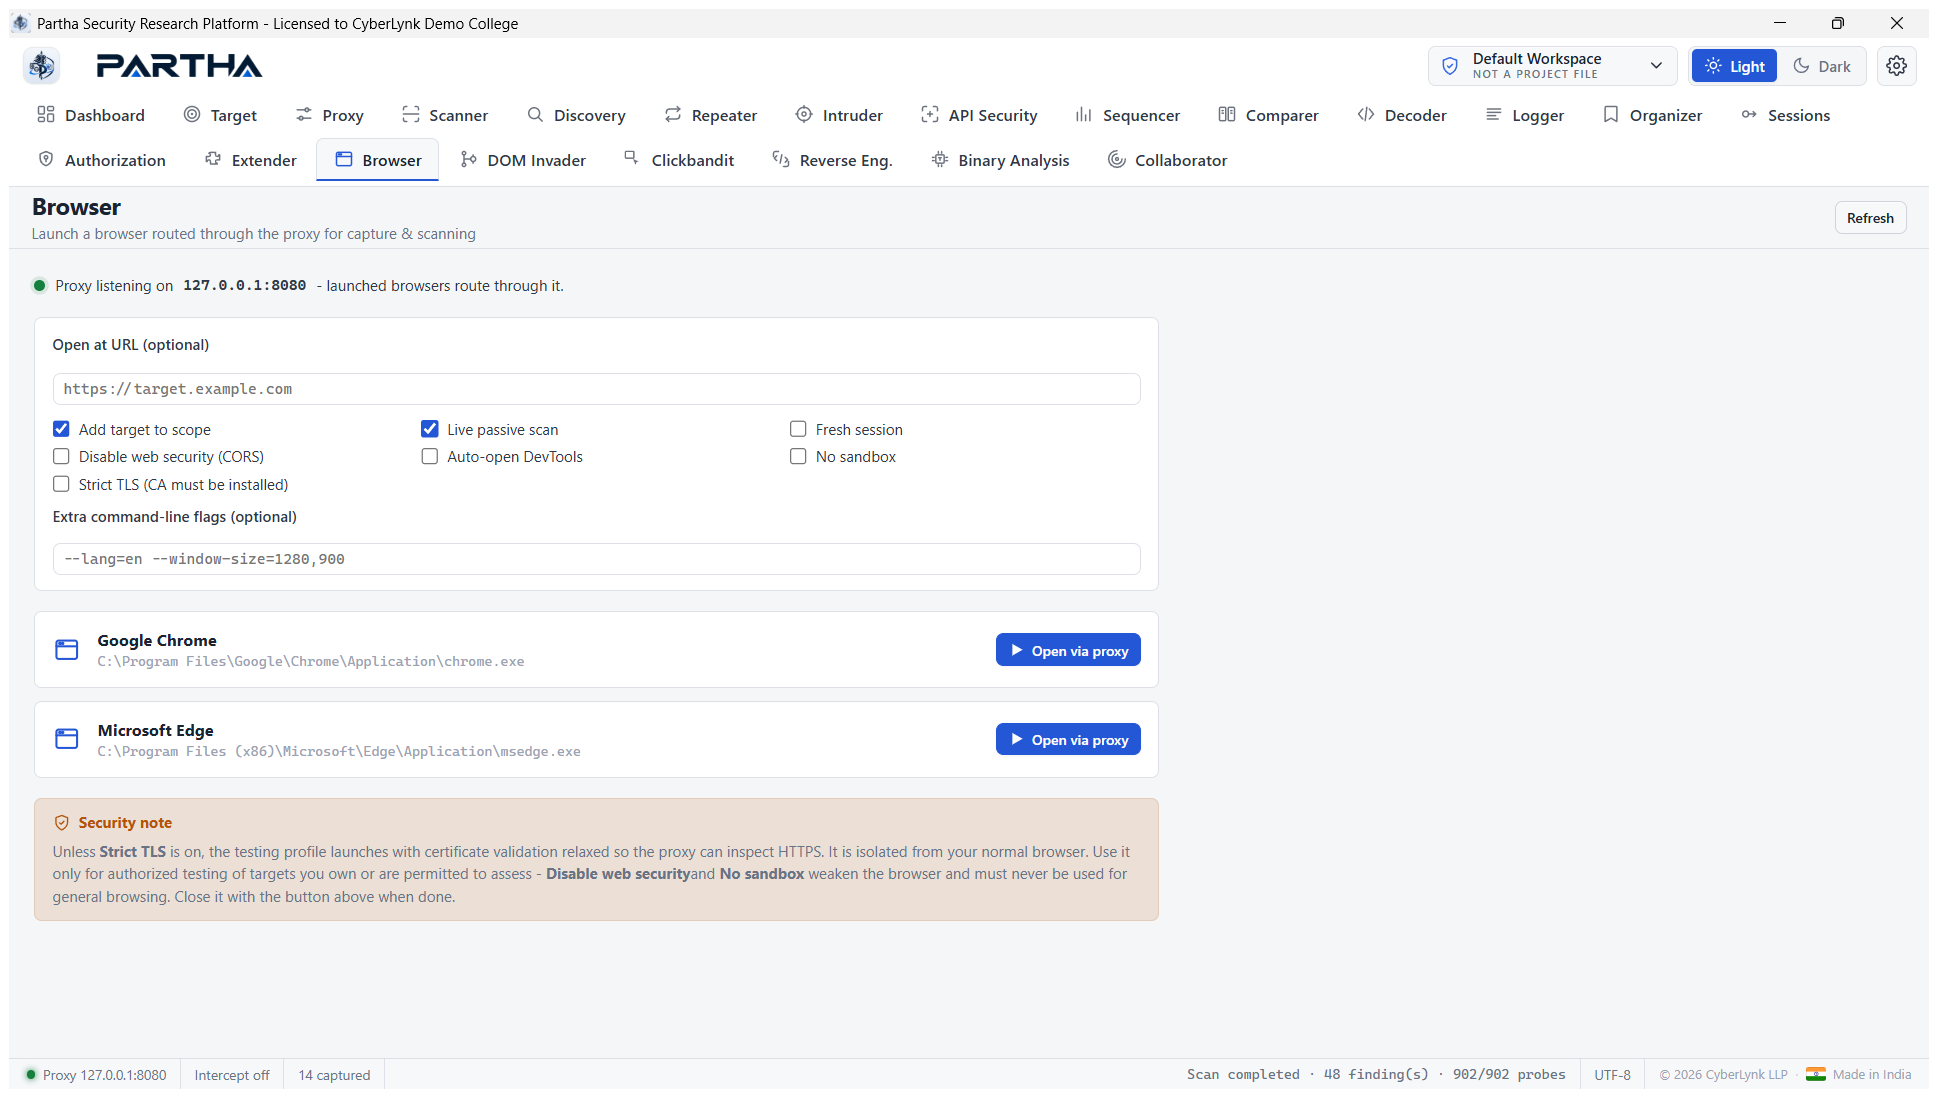
Browser — built-in browser
Scan using a built-in browser that navigates JavaScript-heavy apps and SPAs just like a user, routed through the proxy.Browser launcherPartha detects installed Chromium-family browsers and…
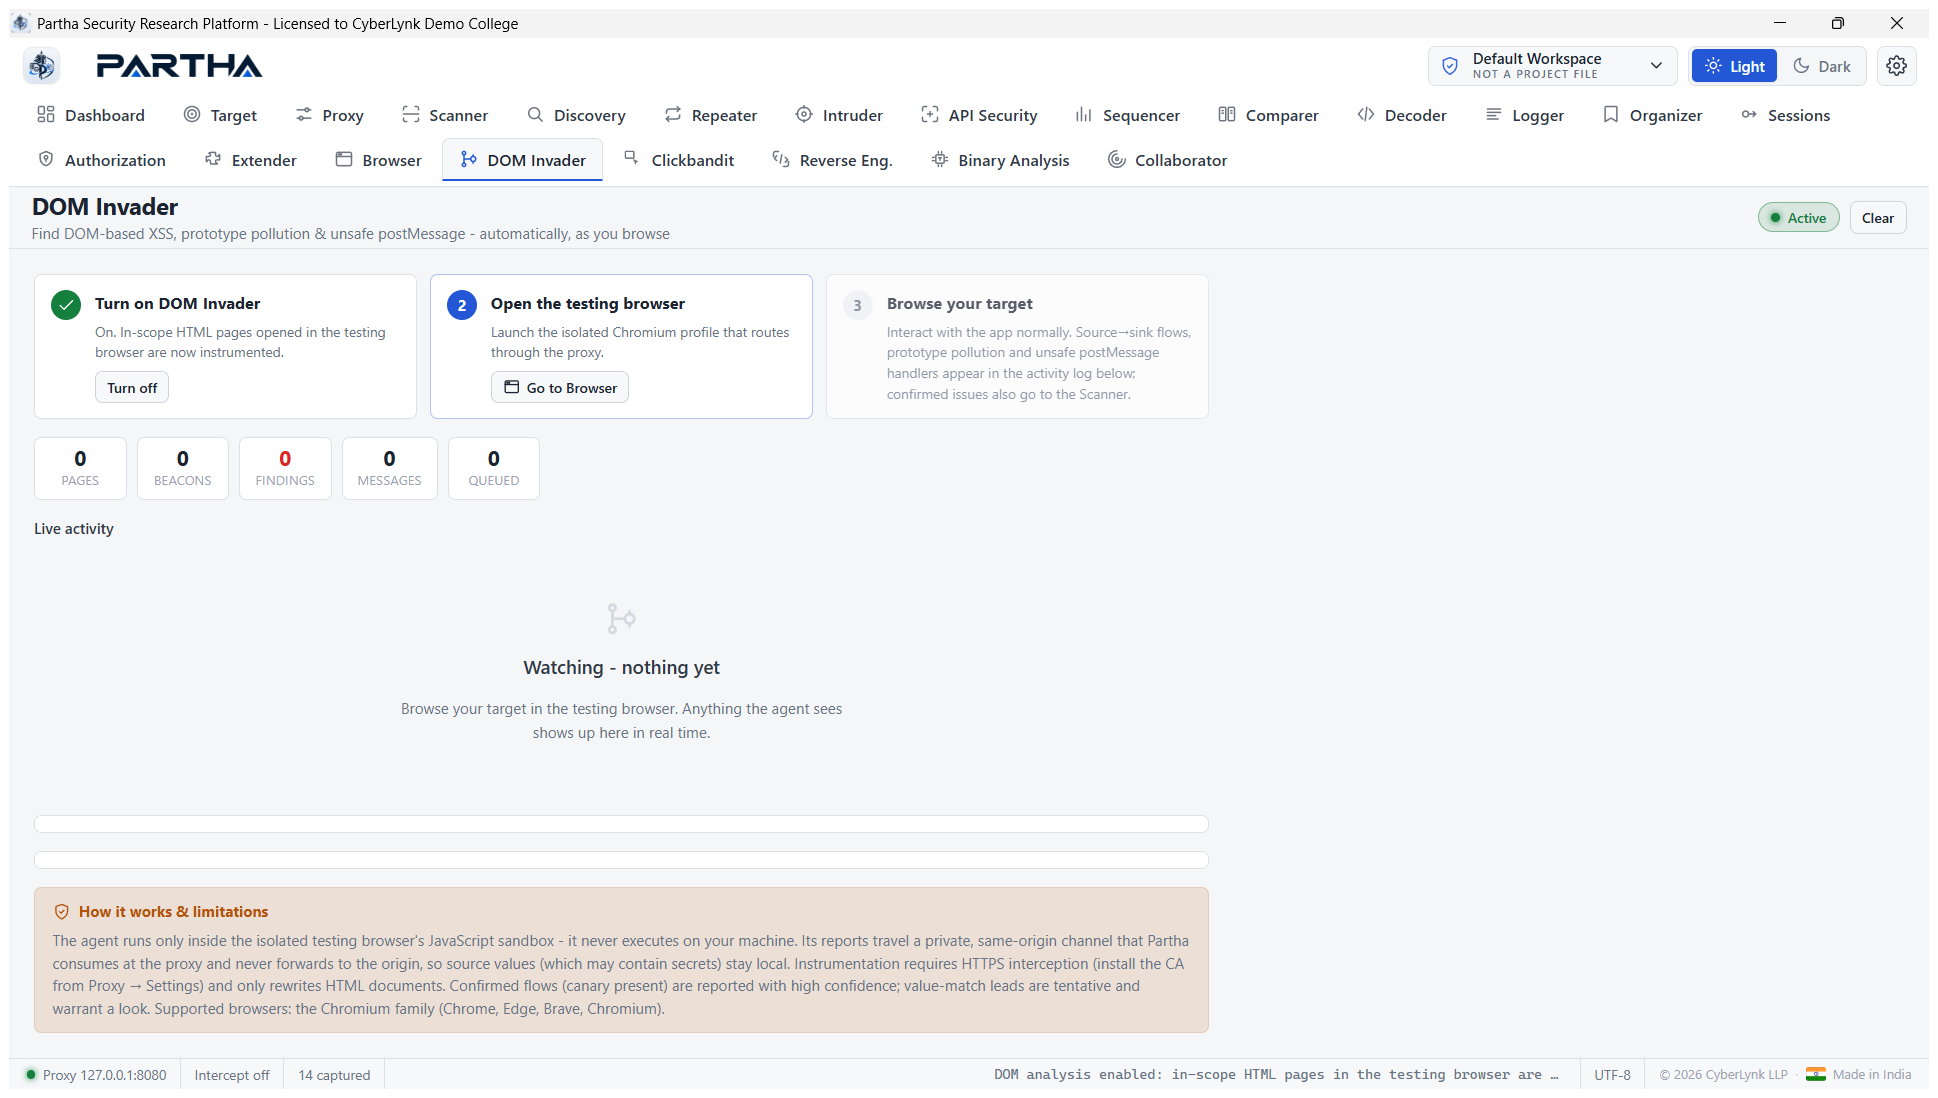
DOM Invader
Test for DOM-based vulnerabilities — DOM-XSS, prototype pollution and unsafe postMessage, automatically, as you browse.The three-step wizard, shown Active (green) after turning it on —…
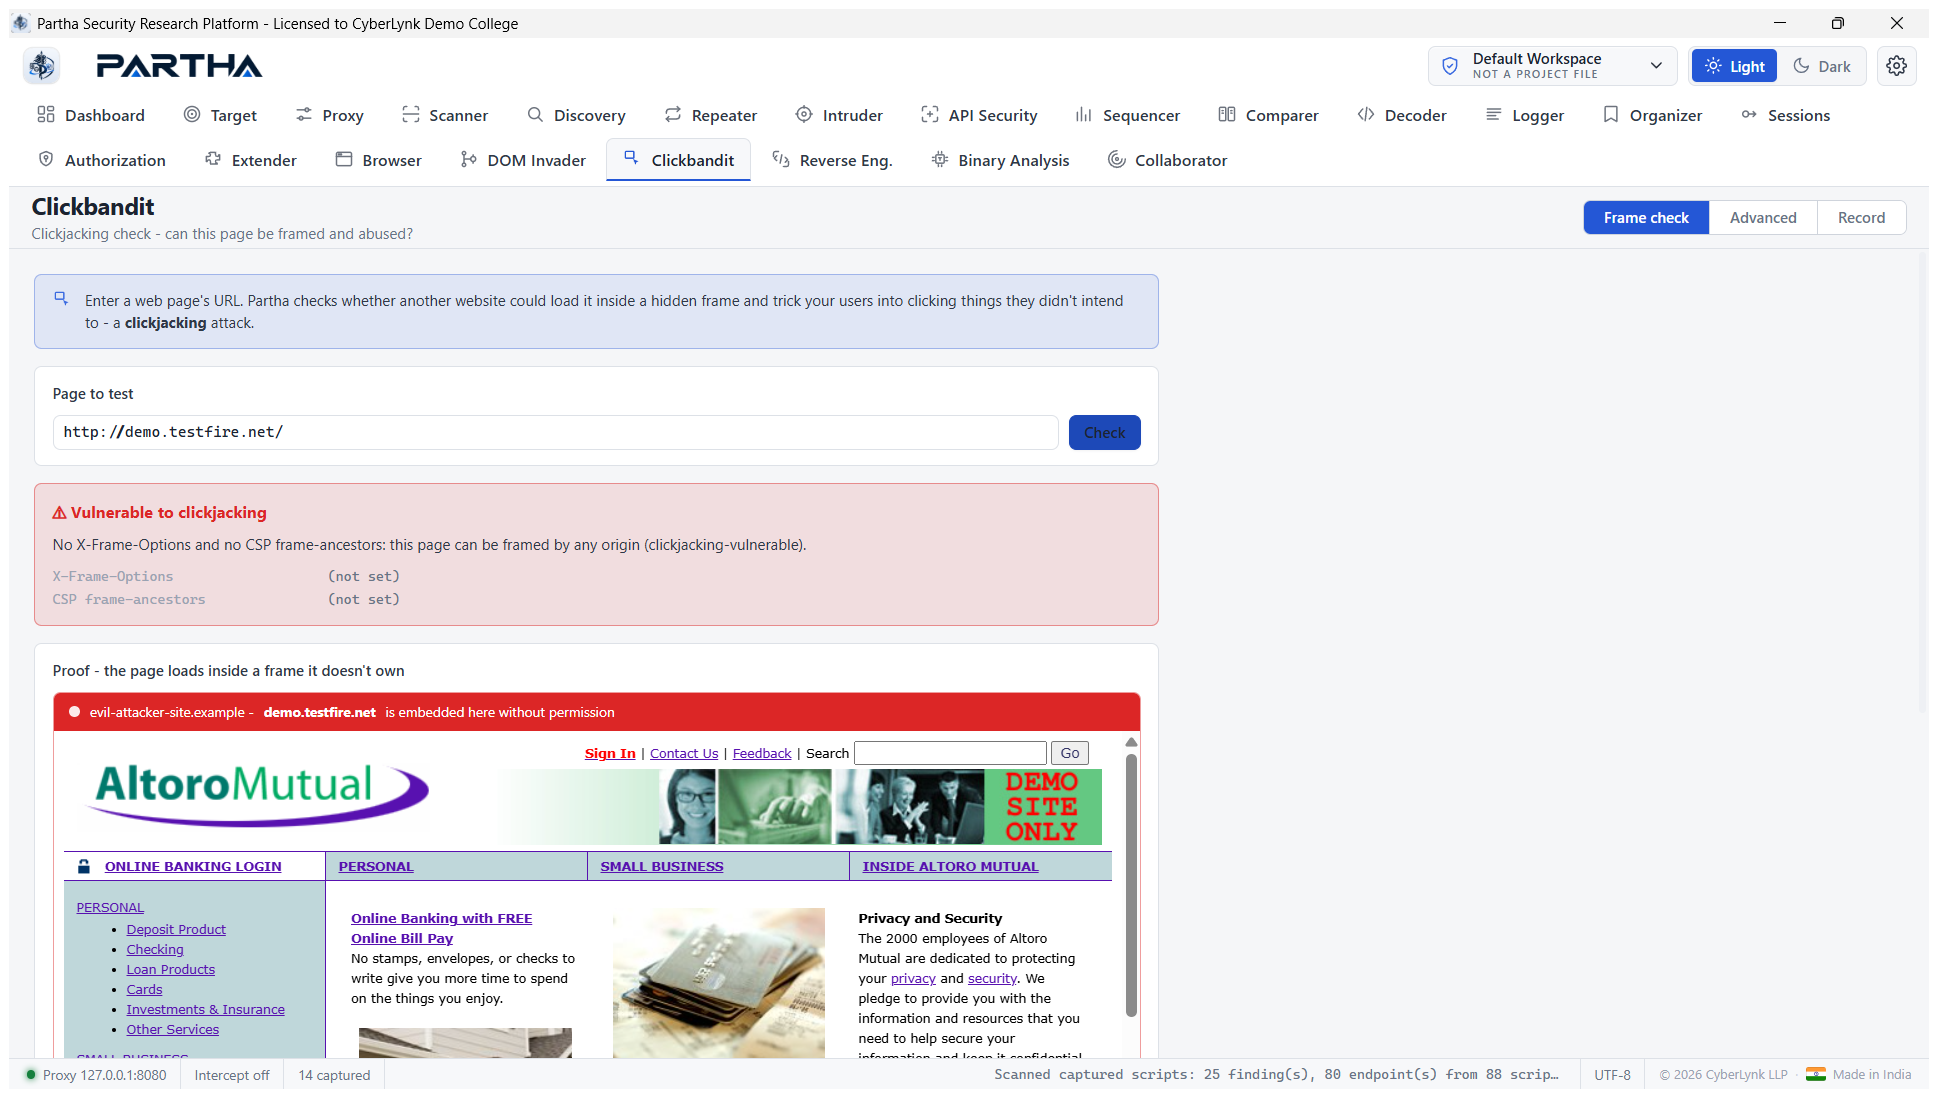
Clickbandit — clickjacking & CSRF PoC
Easily generate proof-of-concept attacks.Frame check — enter a URL and Check. For http://demo.testfire.net/ the real verdict is ⚠ Vulnerable to clickjacking (no X-Frame-Options, no CSP…
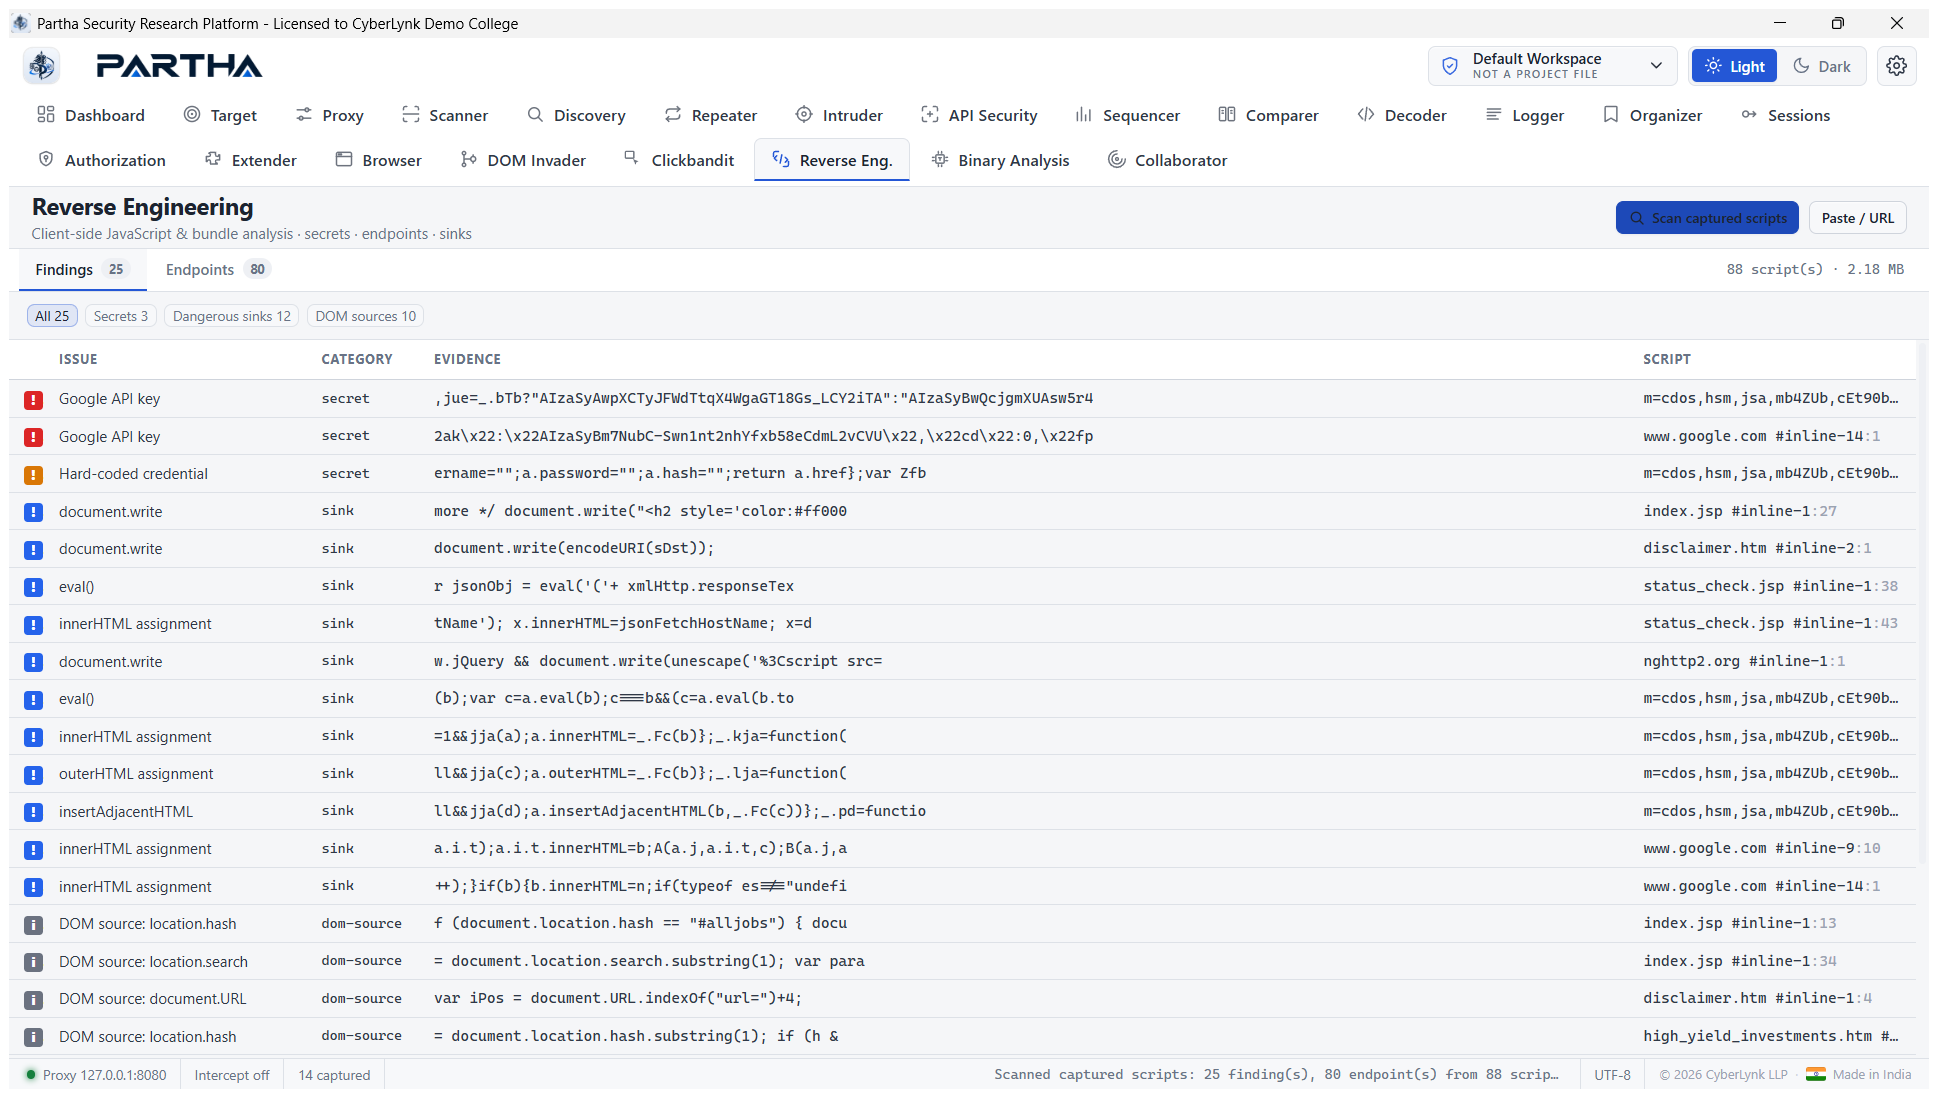
Reverse Engineering — JavaScript analysis engine
Conquer client-side attack surface with the built-in JavaScript analysis engine — statically analyse captured scripts (external .js and inline <script>) for secrets, endpoints and dangerous…
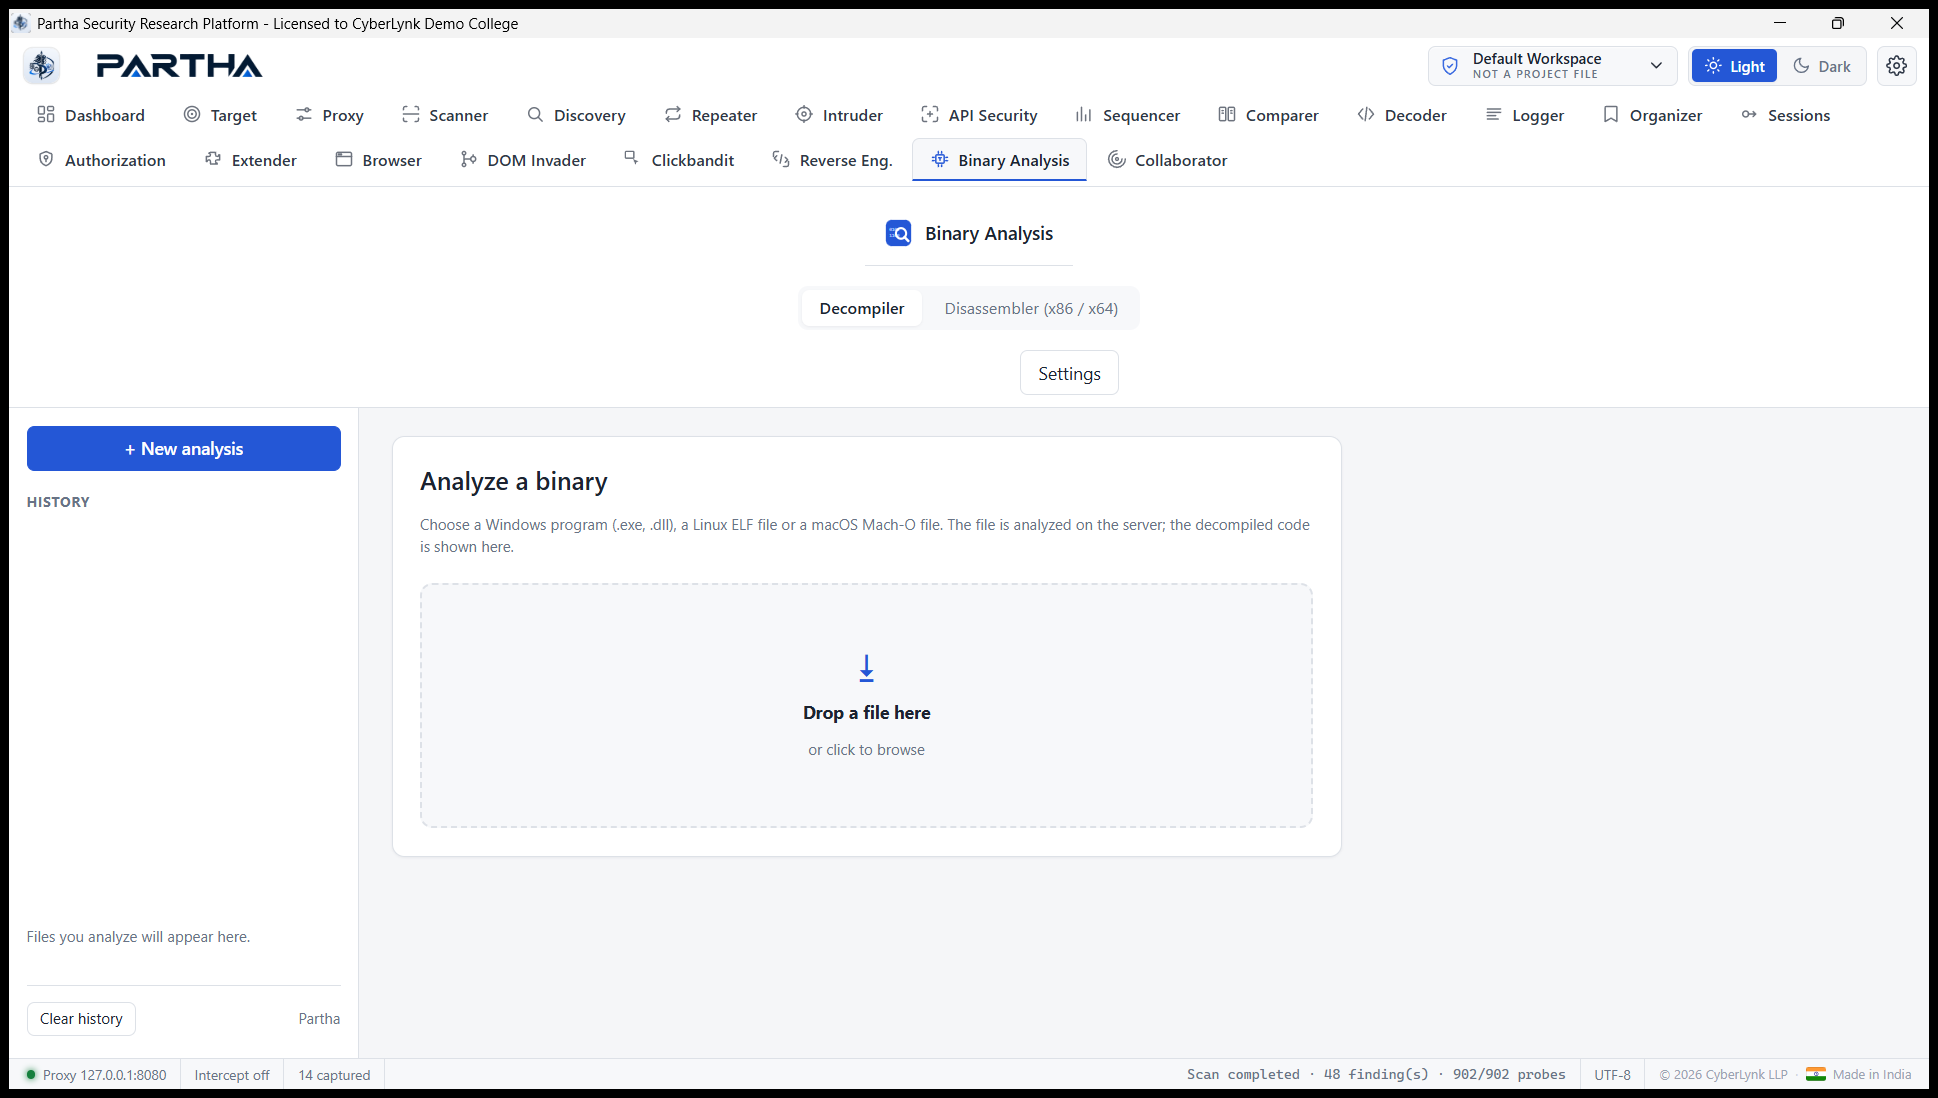
Binary Analysis — disassembler & cloud decompiler
A first-class binary reverse-engineering module with two independent surfaces:Binary AnalysisDisassembler (x86 32/64) — entirely on this PC. Real result — disassembling a real Windows PE…
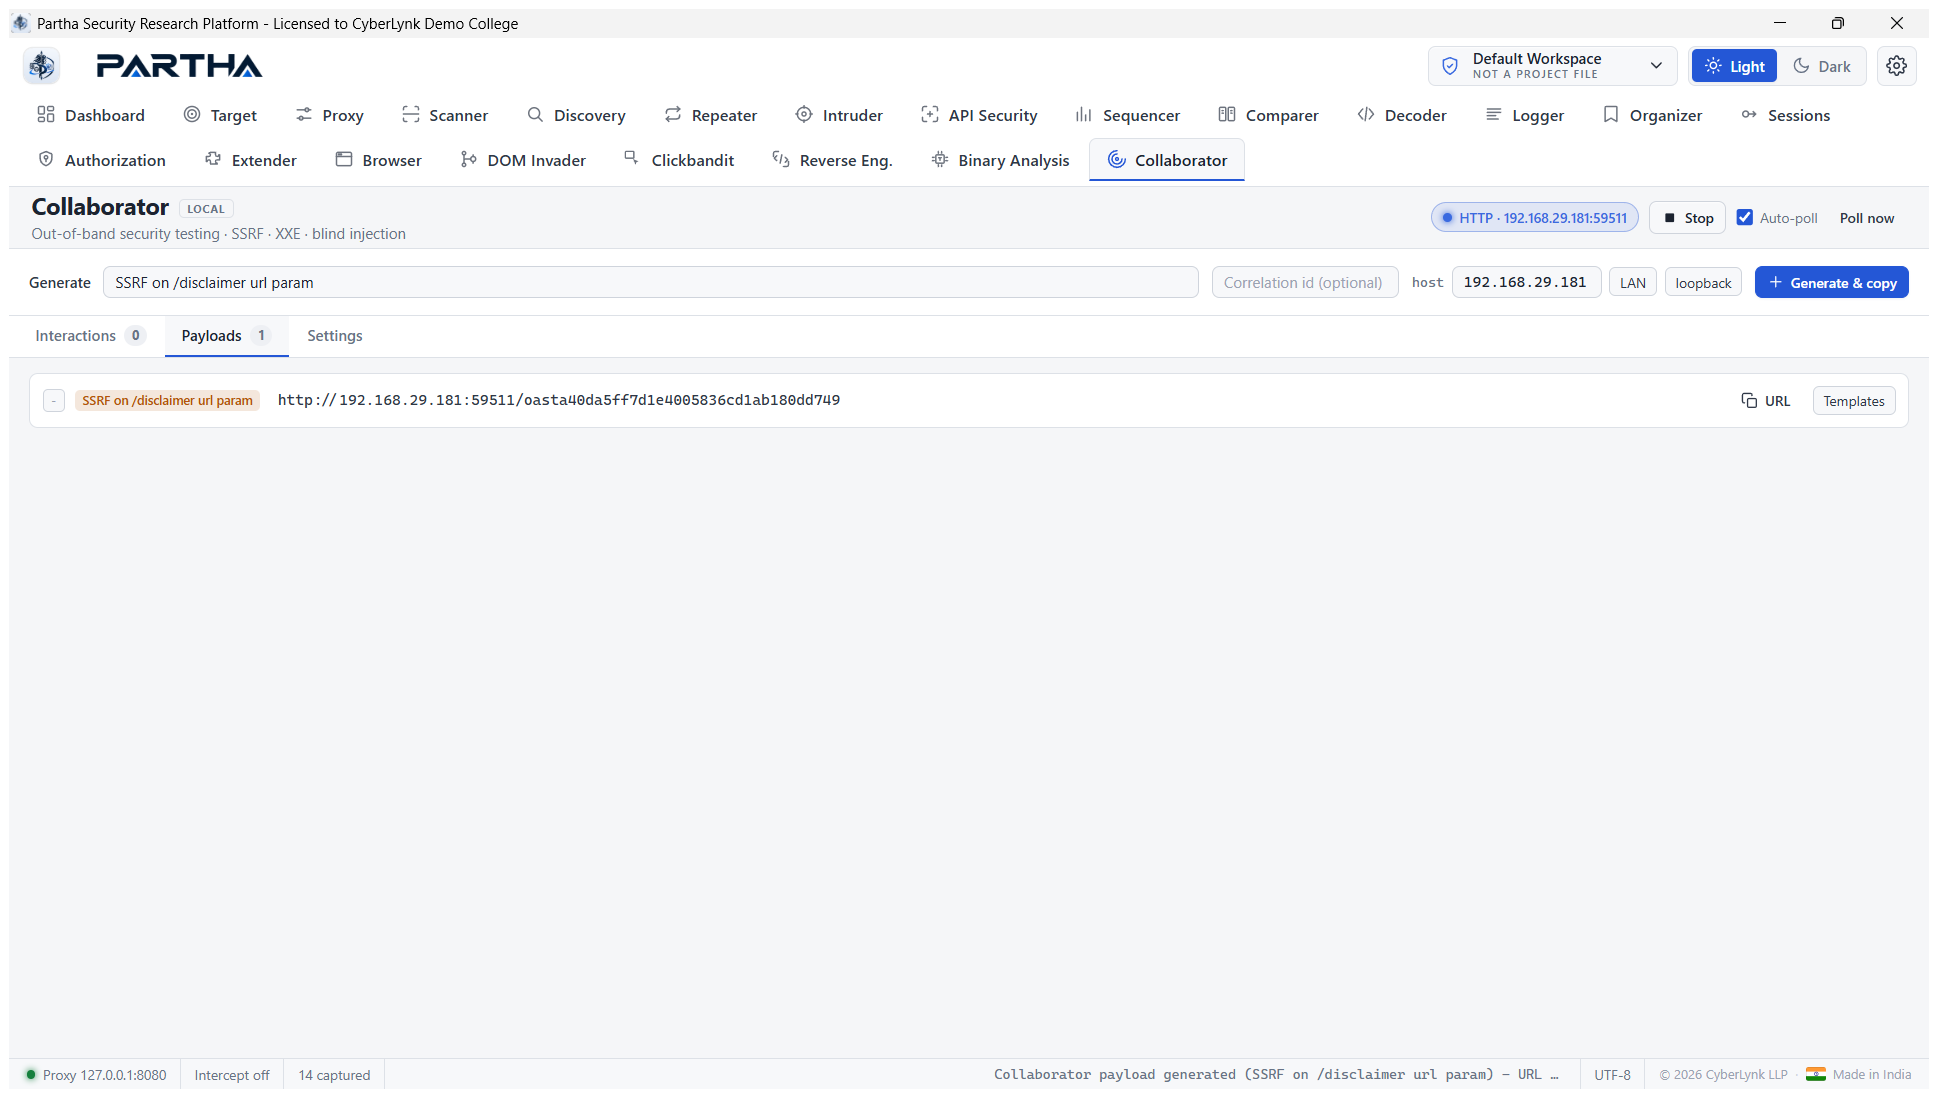
Collaborator — OAST
Detect otherwise-invisible vulnerabilities with out-of-band application security testing (OAST). Partha runs its own listener (HTTP + DNS + SMTP).Generate a payload — with an optional note,…